

CD Projekt Red released an urgent patch for Cyberpunk 2077 to fix a remote code execution vulnerability that could be exploited by third‑party data file modifications and store game files.
On February 2, 2021, CD Projekt warned Cyberpunk 2077 users to avoid using files, such as mods that modify data files or custom game save files, due to a vulnerability in the way the game uses DLL files.

Last week, CyberpunkSaveEditor creator PixelRick revealed that a buffer overflow vulnerability allows modifications that allow remote code execution on a computer.
ASLR is a security feature that randomizes the memory areas (address space) used by a process. In this way, vulnerability exploits must be tailored to a specific process as it is loaded into memory.
If exploited, this vulnerability could allow attackers to execute commands on the computer, including downloading and installing malware.
To resolve the vulnerabilities, CD Projekt released the Cyberpunk 2077 1.12 hotfix, which states that “Fixed a buffer overrun issue” and “Removed/replaced non-ASLR DLLs.”
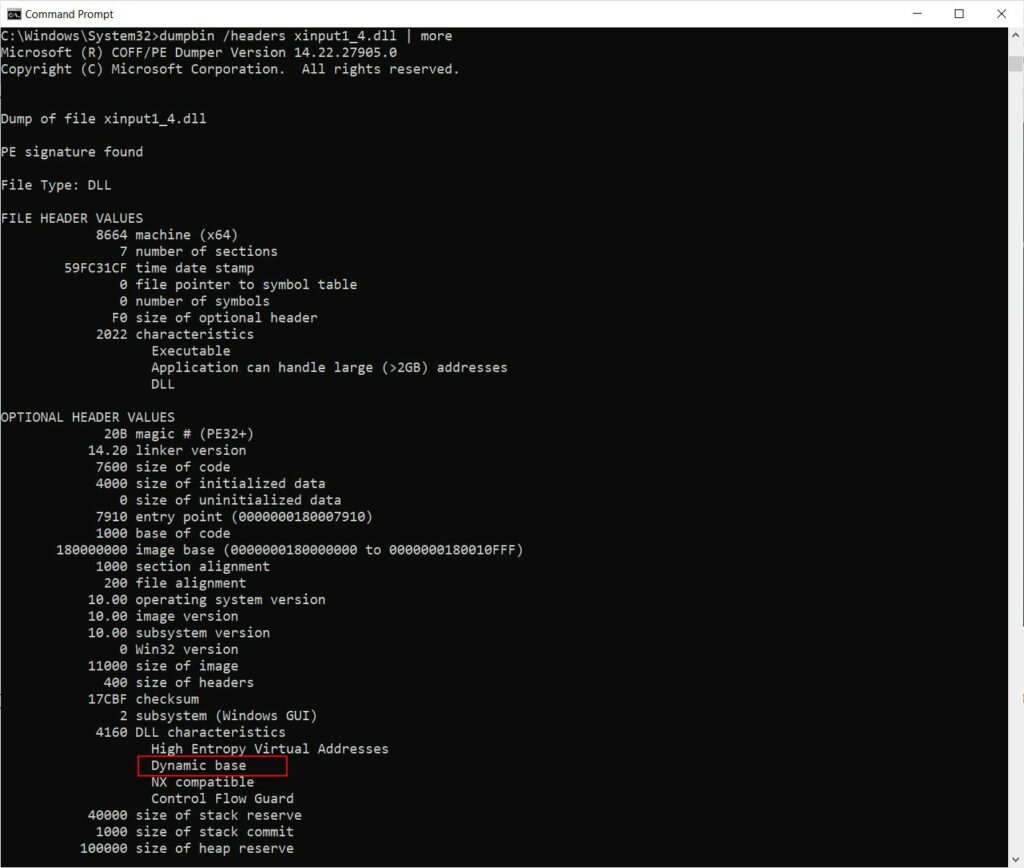
With this hotfix, the vulnerable DLL file xinput1_3.dll is removed and the Cyberpunk2077.exe executable loads the ASLR-enabled C:\Windows\System32\xinput1_4.dll file in conjunction with Windows 10 .
The ASLR feature appears to be enabled in the xinput1_4.dll file with the "dynamic base" attribute displayed using the "dumpbin.exe /headers" command, as shown below.
If you are launching Cyberpunk 2077 outside of Steam or using a mod manager, it is recommended that you update the game first on Steam before playing. The patch is small and only takes a few seconds to install.
Information source: bleepingcomputer.com
