

 One of the largest web hosting providers, Hostinger ,announced that a security, which affected the platform and users .
The company made the announcement in a blog post. In it, it said that a hacker managed to gain access to an internal server. There, he found a token that gave him access to an internal API.
According to the company, the hacker used the API to gain access to a database of that stores the personal information approximately 14 million customers. Some of the information stored in this database includes Hostinger usernames, customers' IP addresses, customers' full names and contact information , such as phone numbers, emails , and home addresses. In addition, users' passwords are stored in hashed form
Hostinger discovered that some of its customers were affected by the hacker attack, so it decided to reset the passwords on all affected accounts.
Many users reported receiving emails or Twitterinforming them of password resets.
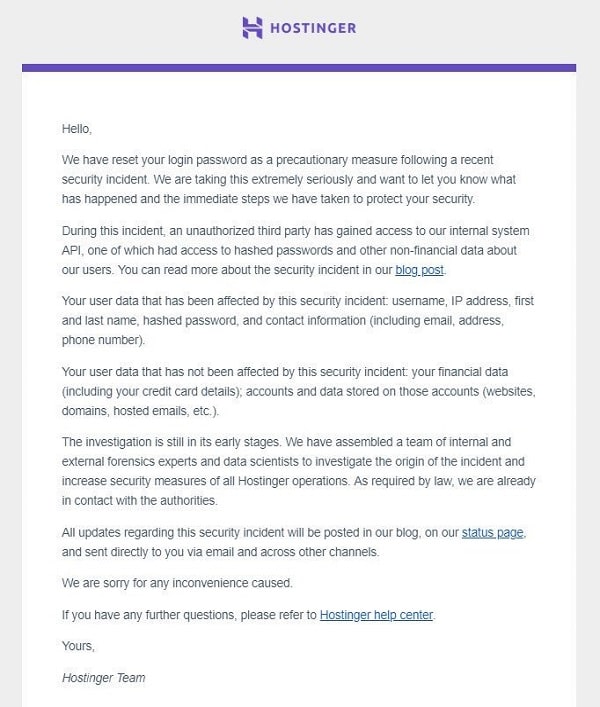
According to Hostinger, the hacker was unable to gain access to financial data and customer sites
The security issue was discovered on Friday, August 23. Hostinger has created a page where customers can see all updates regarding this breach.
The company said the compromised server and API have been removed.
“Our central system's API server has been damaged and we know that the intruders may be extracting data directly from the database”, said the company's CEO, Balys Kriksciunas.
“We had to make quick decisions», he added. “We have reset the passwords of all customers that were affected by the API server breach”.
The company stated that it is not in a position to disclose more at this time, given that it is a very early stage of the investigation and new data may emerge.
