

The Emotet botnet has started using a new template for its malicious attachments, and it is just as dangerous as the ones it used in the past.
After a five-month “holiday,” the Emotet malware returned in July 2020 and began spreading huge amounts of spam worldwide.
These spam campaigns pretend to be invoices, shipping information, COVID-19, resumes, or financial documents.
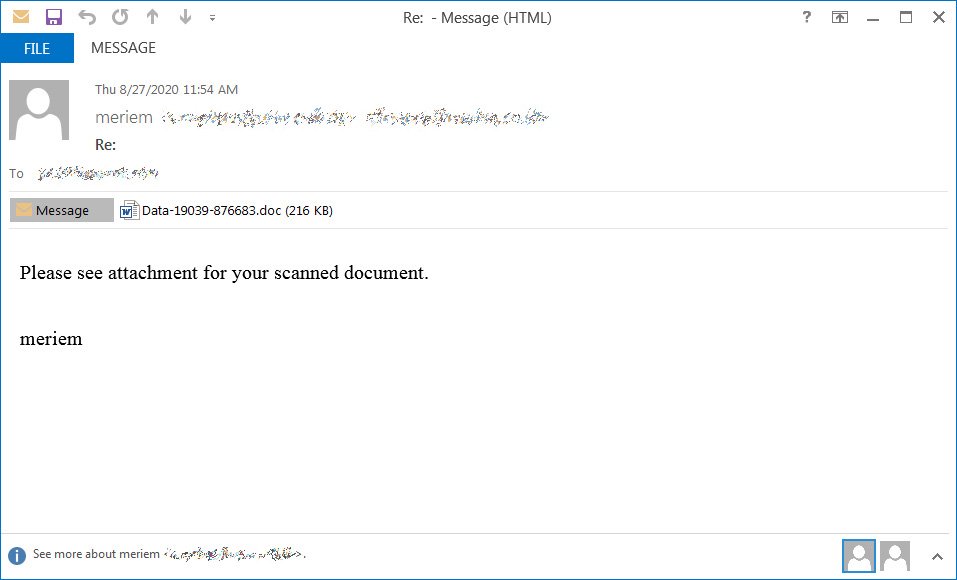
These spam emails contain malicious Word (.doc) attachments or download links.
When opened, these attachments ask the user to enable "Enable Content" so that malicious macros can be executed to install the Emotet malware on the victim's computer.
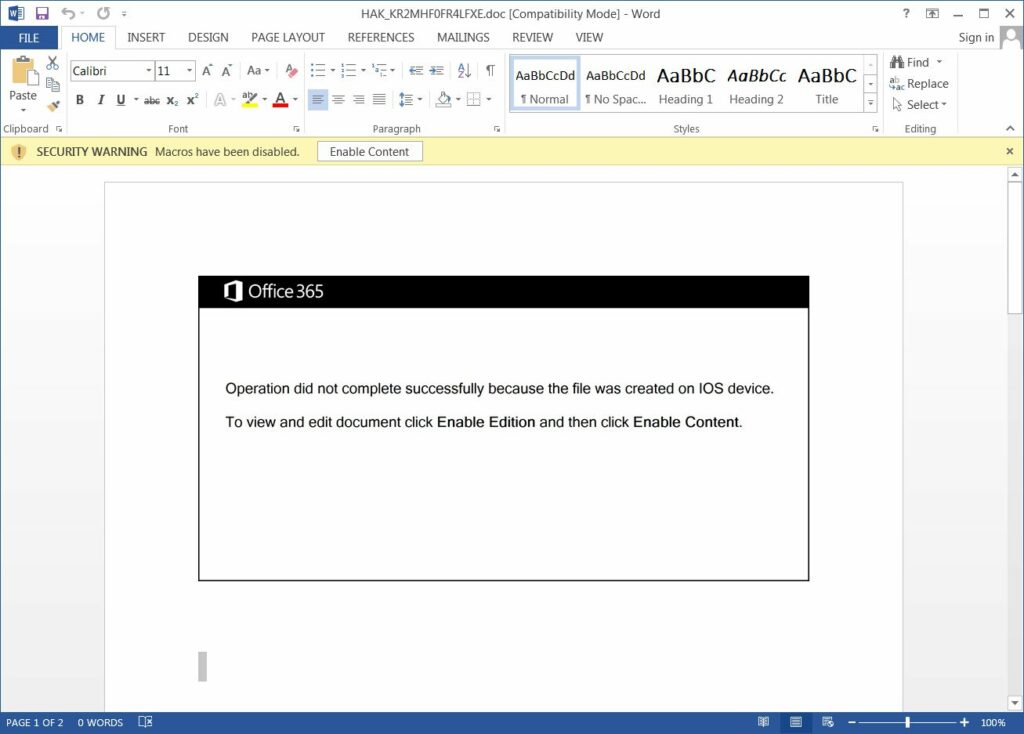
To trick the user into enabling macros, Emotet uses a document template that says the document was created on iOS and cannot be viewed properly unless the "Enable Content" button is pressed.

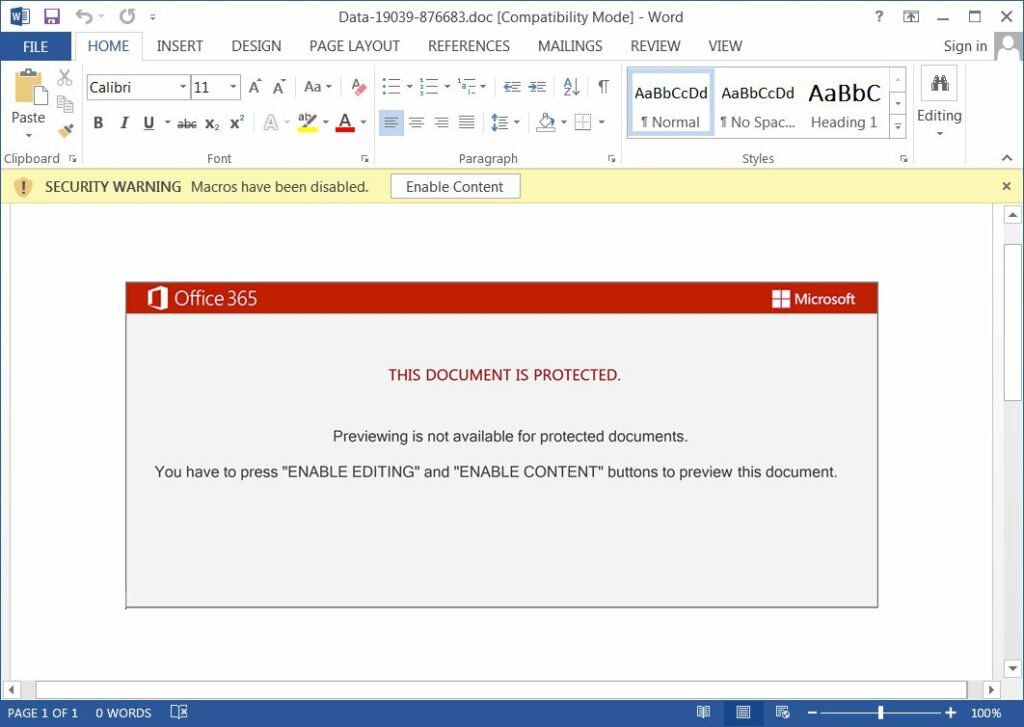
On August 25, the botnet changed template which Emotet expert Joseph Roosen named "Red Dawn" due to its red colors.
The Red Dawn template does not use the iOS argument and states that “This document is protected” but preview.
It then asks the user to click on “Enable Editing” and “Enable Content” to view the document.
Like the previous template, once the user clicks on the content, malicious macros will be executed that will download and install the Emotet malware on computer .
Why is it necessary to recognize Emotet attachments?
Emotet is considered the most widespread malware targeting users. It is also particularly harmful, as it will install other dangerous malware such as Trickbot and QBot on a victim's computer.
While TrickBot and QBot can perform different malicious activities, both will attempt to steal saved passwords, cookies, banking information, and various other sensitive information from the victim's computer.
To make matters worse, both trojans are known to provide access to hackers who install ransomware like Conti (TrickBot) or ProLock (QBot) across the network.
Because of this, it is vital that you are able to identify the malicious document templates that Emotet uses so that you do not accidentally get infected.
