

Malicious hackers are actively exploiting a high-severity vulnerability in Openfire messaging servers to encrypt servers with ransomware and install cryptominers.
Openfire is a widely used open source Java-based chat server (XMPP) that has been downloaded 9 million times and is used extensively for secure multi-platform chat communications.
The flaw, identified as CVE-2023-32315, is an authentication bypass that affects the Openfire management console, allowing attackers to create new administrator accounts on vulnerable servers.
Using these accounts, attackers install malicious Java plugins (JAR files) that execute commands received via GET and POST HTTP requests.
This dangerous flaw affects all Openfire versions from 3.10.0, dating back to 2015, to 4.6.7 and from 4.7.0 to 4.7.4.
Although Openfire fixed the issue with versions 4.6.8, 4.7.5, and 4.8.0, released in May 2023, VulnCheck reported that as of mid-August 2023, more than 3,000 Openfire servers were still running a vulnerable version.
Dr. Web is now reporting signs of active exploitation, as hackers have taken advantage of the attack surface for malicious campaigns .
The first case of active exploitation detected by Dr. Web dates back to June 2023, when the security firm investigated a ransomware attack on a server that occurred after exploiting CVE-2023-32315 was used to compromise the server.
Attackers exploited the vulnerability to create a new admin user in Openfire, logged in, and used it to install a malicious JAR add-on that can execute arbitrary code.
Some of the malicious JAVA plugins that Dr. Web and customers have seen include helloworld-openfire-plugin-assembly.jar, product.jar , and bookmarks-openfire-plugin-assembly.jar.
After creating an Openfire honeypot to capture the malware, Dr. Web recovered additional trojans used in attacks.
The first of the additional payloads is a Go- based crypto-mining trojan , known as Kinsing.
Its operators exploit CVE-2023-32315 to create a handler named “OpenfireSupport” and then install a malicious plugin named “plugin.jar” that retrieves the miner payload and installs it on the server.
In another incident, attackers installed a UPX-compressed backdoor written in C language, following a similar infection chain.
A third attack case observed by Dr. Web analysts is where a malicious Openfire plugin was used to obtain information about the compromised server, specifically network connections, IP addresses , user data , and the system kernel version
Dr. Web identified a total of four distinct attack scenarios that exploit CVE-2023-32315, making it imperative to apply available security updates.

An unknown ransomware
The website BleepingComputer reported several reports from customers who reported that their Openfire servers were encrypted with ransomware, with one reporting that files were encrypted with the .locked1 extension.
Since 2022, a threat actor has been encrypting exposed web servers with ransomware that appends the .locked1 extension.
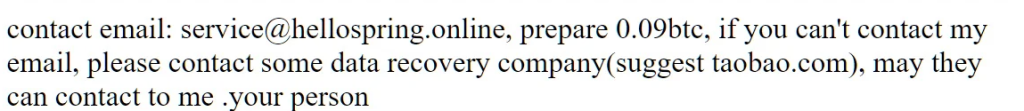
BleepingComputer is aware that Openfire servers were encrypted by this ransomware in June.
It is unclear what ransomware is behind these attacks, but ransom demands are generally small, ranging from 0.09 to 0.12 bitcoins ($2,300 to $3,500).
The malicious actor does not appear to be focused exclusively on Openfire servers, but rather on any vulnerable web server. Therefore, applying all security updates to your servers as they become available is crucial.
Information source: bleepingcomputer.com
