

Security researchers discovered a ransomware attack that tries to recruit members for the Russian mercenary group Wagner, which rebelled briefly against the Kremlin last weekend.
See also: New Mockingjay process injection technique evades EDR detection

The ransomware is designed to target Windows computers and leaves a note suggesting victims should consider joining the paramilitary group, according to security firm Cyble.
“Job opening. Service in the PMCS Wagner. For cooperation,” the note states, later adding: “Brothers, stop tolerating authority! Let's go to war against Shoigu!”—a reference to the military general under Russian President Vladimir Putin.
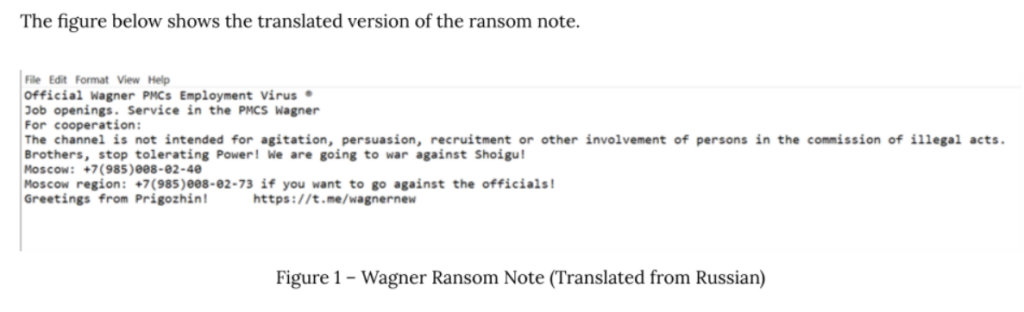
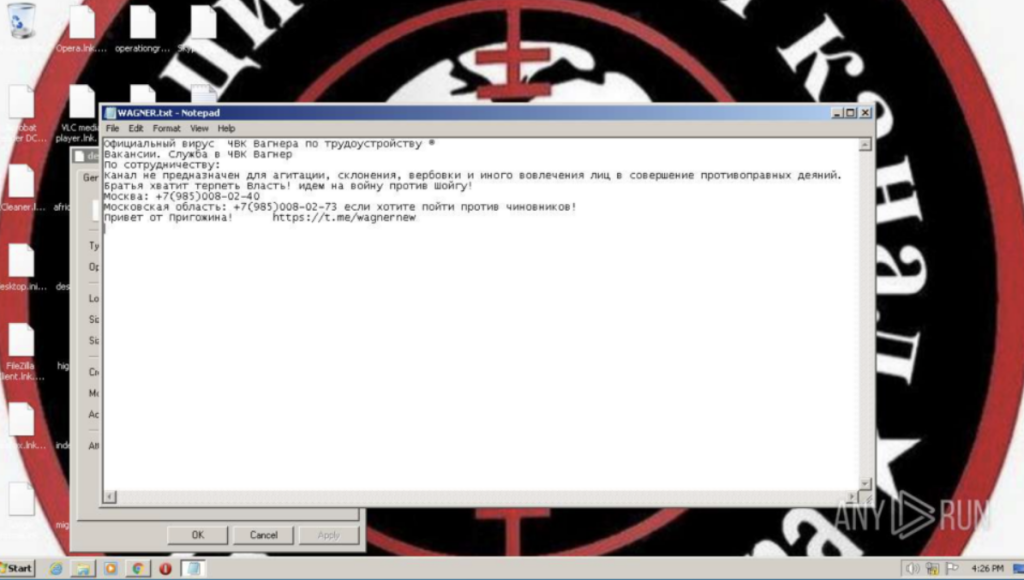
The note is written in Russian, indicating that the ransomware was created to target computers in the country. Cyble also observed the attack after a sample of the ransomware was uploaded to VirusTotal by a user in Russia. The same note includes a real phone number for Wagner's recruitment offices in Moscow, accompanied by the phrase “if you want to go against the officials!”
See also: MOVEit attacks: Siemens Energy confirmed data breach
The ransomware appeared last weekend exactly at the moment when Yevgeny Prigozhin, the leader of Wagner, ordered his troops to move towards Moscow in an attempt to remove Shoigu from the Russian Ministry of Defense. A few hours later, Prigozhin defeated the armed uprising, simultaneously accepting an agreement that would essentially exile him to Belarus.
It is not clear who created the ransomware core. Wagner has not taken responsibility for the malicious code. Furthermore, it appears that the attack was created using the Chaos ransomware creation tool, which first appeared on dark forums.
It is interesting that, while the attack encrypts various files on a Windows computer, the ransom note does not require the victim to pay. Thus, it appears that the attack can permanently destroy the files on an infected computer.
Cyble concluded: “the person behind the ransomware stem could have political motives and support the Wagner group”. However, Allan Liska, security researcher at Recorded Future, suspects that the real intent may be different.
“Installing ransomware or a wiper on someone's machine is a bad way to recruit them”, said Liska in a tweet. “On the other hand, if you are a hacktivist group – let's say one that has used ransomware based on the Chaos Builder in the past – that wants to enrage the world with a specific group, this is an effective way to do it&rdquo.
See also: The removal of EncroChat led to 6,600 arrests of criminals
The method of propagation of the Wagner ransomware also remains unclear. However, currently, most antivirus protection programs detect the attack as malicious, according to VirusTotal.
Information source: pcmag.com
