

Microsoft announced that its Edge Vulnerability Research team is experimenting with a new feature called “Super Duper Secure Mode” that is designed to bring security improvements without significant performance losses.
When enabled, the new Microsoft Edge Super Duper Secure Mode will remove Just-In-Time (JIT) compilation from the V8 processing pipeline, reducing the factors that threat actors can use to compromise Edge users' systems.
See also: Motorola announces Edge 20, 20 Pro & Edge 20 Lite phones

See also: Microsoft releases Sleeping Tabs in Edge
Security without much success
Based on CVE (Common Vulnerabilities and Exposures) data collected since 2019, approximately 45% of vulnerabilities identified in the V8 JavaScript and WebAssembly engines were related to the JIT engine.
Additionally, while the JIT compiler is designed to increase performance by compiling the computer while the program is running, disabling it in Super Duper safe mode "does not always have negative effects.".
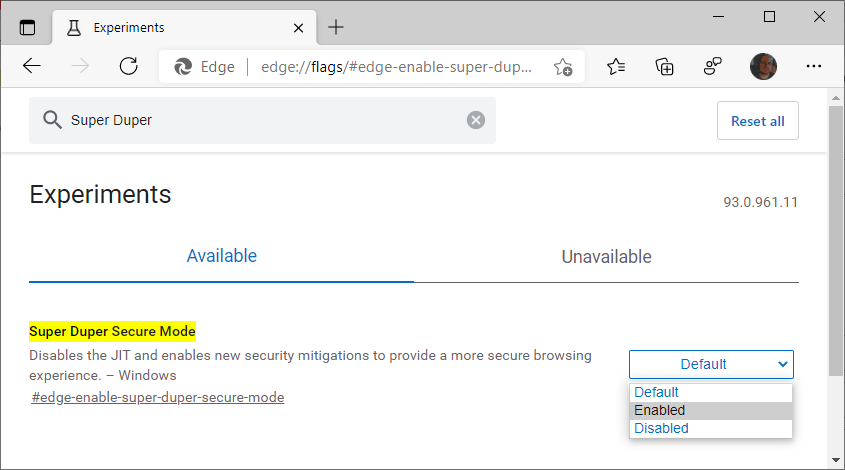
While still in the experimental stage, Super Duper Secure Mode can be enabled by users of preview versions of Microsoft Edge (including Beta, Dev, and Canary) by going to edge://flags/#edge-enable-super-duper-secure-mode and toggling the new feature.
See also: Twitter: Testing new Edge-to-Edge timeline layout
Currently, when enabled, Super Duper Secure Mode disables JIT (TurboFan/Sparkplug) and enables Control-flow Enforcement Technology (CET), an Intel hardware-based exploit mitigation designed to provide a more secure browsing experience.
In the future, Microsoft also wants to add support for Arbitrary Code Guard (ACG), another security mitigation that would prevent malicious code from being loaded into memory, a technique used by most web browser exploits.
Information source: bleepingcomputer.com
