

 Researchers at AdaptiveMobile Security have discovered a critical vulnerability cards SIM. It is a zero-day vulnerability called SimJacker that allows hackers to remotely compromise mobile phones and spy on victims by simply sending an SMS.
The SimJacker vulnerability has been identified in the S@T (SIMalliance Toolbox) Browser that is embedded in most SIM cards in about 30 countries. According to researchers, hackers can exploit this vulnerability regardless of the victim's phone model.
Researchers discovered that a private surveillance company had known about the SimJacker vulnerability for at least two years and was exploiting it to spy on users in multiple countries. According to AdaptiveMobile Security, the company works with various governments.
The S@T Browser application is built into many SIM cards (and eSIMs). It is part of the SIM Tool Kit (STK).
S@T Browser is capable of implementing a range of instructions, such as sending messages, making calls, launching the browser, providing local data, executing commands, and sending data.
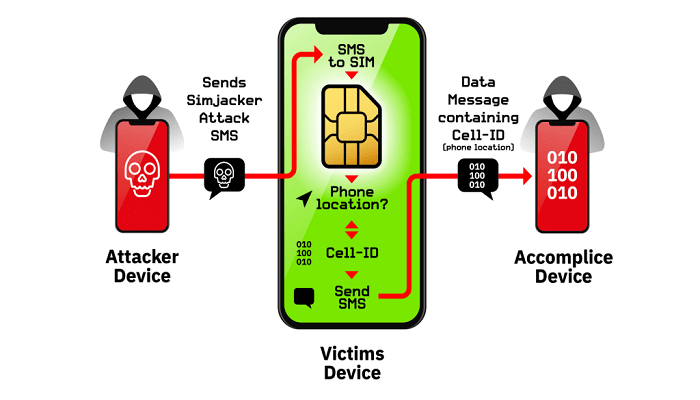
The Simjacker vulnerability allows a hacker to send an SMS with commands that can direct the SIM card of a victim's phone. This way, the attacker can take control of the phone.
What could the attacker do using the vulnerability?
Attackers could do many things once they take control of victims' mobile phones. They could learn the victims' location and IMEI information and gain access to all the information on the device. In addition, they could send fake messages to spread misinformation, commit various scams, spread malware and carry out denial-of-service attacks.
According to researchers, victims cannot perceive suspicious activities.
“The Simjacker attack involves an SMS that contains a specific type of spyware code and is sent to a mobile phone. It then gives a command to the SIM card to take control of the phone to execute commands», researchers said.
“During the attack, the victim user completely ignores that they fell victim to an attack and that information was stolen».
Researchers have detected SimJacker attacks on the most popular mobile phones, including those from Apple, Google, Huawei, Motorola, and Samsung.
Experts are very concerned because almost any mobile phone model is vulnerable to the SimJacker attack.
“The Simjacker vulnerability could affect over 1 billion mobile phone users worldwide».
“The Simjacker vulnerability poses a clear risk to mobile services and subscribers. It is perhaps the most sophisticated attack ever seen on mobile networks ,” said Cathal McDaid, CTO of AdaptiveMobile Security
He then said that the Simjacker vulnerability has been used successfully for years because it exploited a combination of complex interconnections and various technologies. Now that this vulnerability has been revealed, increasingly more cybercriminals will try to use it in other areas.
Hackers are constantly finding new and more complex ways to undermine network security , putting customers, mobile phone companies, and a country's national security at risk
Researchers fear that now that the SimJacker vulnerability has been revealed, many hackers will try to use and exploit it.
