

As we all know, cryptocurrency mining is an expensive process. In fact, to be considered profitable in the long run, it requires investment in hardware and space. But let's be realistic, the cost of electricity is always exorbitant and after a while, really unprofitable.
This conclusion has led many hackers to decide to use, in some way, the equipment of others. Beyond the legal aspect of the matter, which is of course illegal, this process does long-term harm to the person who unsuspectingly provides equipment to someone.
The main problems are overheating of the computer, resulting in hardware problems and slowing down of processes. We cannot ignore, of course, the “inflated” electricity bills that someone has to pay.
The methods used for cryptocurrency mining are as follows.
Let's start with Web mining. Hackers insert malicious scripts into frequently visited sites or advertisements. They then use computer resources for their own benefit. Last year, for example, such scripts were detected on Youtube.
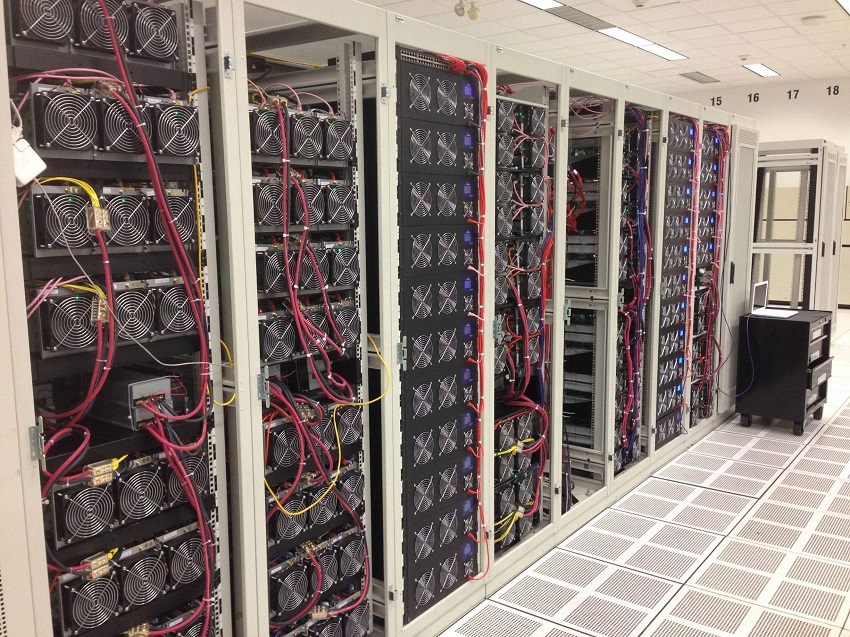
Next, it is worth considering Malicious mining. Malware in systems is not a new problem. In this case, the target is not personal data but cryptocurrency. The practical indication on the computer is reduced performance, which may not be visible for a long time.
Next, we will look at Insider mining. It is perhaps the most dangerous form because it is carried out from the inside. Insider mining is not easily detected because it looks as if a legitimate user initiated the process.
Luckily, there is a way to detect mining. First, you will notice a noticeable drop in performance, and then the temperature will rise due to the overloaded processors.
Because such applications are not necessarily malicious , they are categorized as “potentially unwanted.” Therefore, the administrator should prohibit the use of potentially dangerous software.
