The Working Group for Information Systems Security and Personal Data Protection of the Open Technologies Organization – EL/LAK is organizing seminars for the PANOPTIS 2016 exercise.
On May 23-27, 2016, the annual national cyber defense exercise "PANOPTIS 2016" took place, organized by the Cyber Defense Directorate (D.KYB) of the Hellenic National Defense General Staff, which has been conducted for several years.
The Open Technologies Organization – EL/LAK, with an open call and a talk at FOSSCOMM 2016, assembled a team for the exercise and participated in all episodes. In this context, a series of workshops will be held where each episode will be analyzed in each lab. The seminars are aimed at developers and system administrators interested in security topics.
In this workshop, the first episode of the exercise will be analyzed and the speakers will delve into how the participant is called upon to cope with the episode. It should be noted that members of this particular PANOPTIS team are already participating in the Greek team that will take part in the European Cyber Security Challenge 2016.
The purpose of the seminars is for the team that participated in the exercise to analyze and evaluate the methods it used so that everyone becomes acquainted with the relevant knowledge.
The first workshop entitled “ Web Application Security – Active Response ” will take place on Saturday, November 5, 2016 at 3:00 PM in the large auditorium of the Conference Center of the Hellenic National University of Athens “ Demokritos ” ( Map ) .
To participate in the seminar, registration is required on the specific EL/LAK website: here
A Few Words About the Scenario:
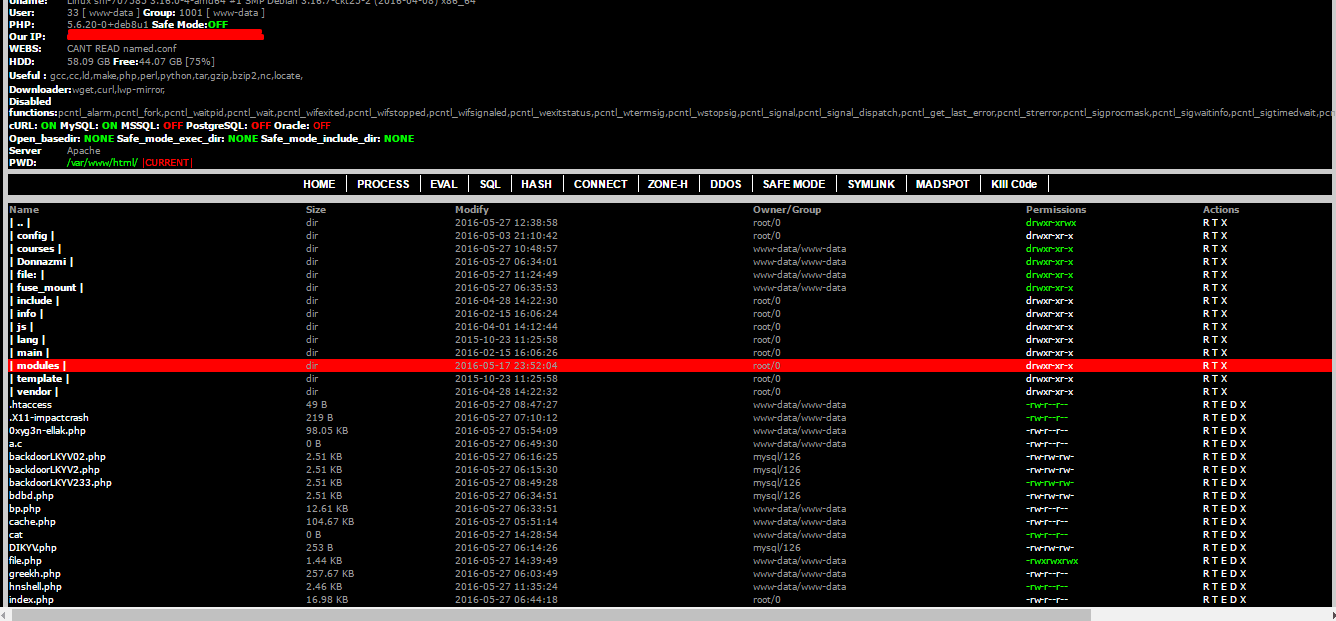
Some malicious attacks result in the disruption of some government network services. Some servers (server hosts) are identified as the source of these attacks. Players are asked to perform an “attack” (gain access) on the already identified targets (servers) in order to terminate the malicious activity…
the continuation… on the screen!