

A hacker claims to have stolen thousands of internal documents containing user records and employee data from Orange Group, a leading French telecommunications provider.
The attacker posted details of the stolen data after unsuccessfully attempting to blackmail the company.
Orange confirmed the breach on BleepingComputer. The company launched an investigation and has taken measures to minimize the impact of the security incident.
The attacker, who uses the pseudonym Rey and is a member of the HellCat ransomware, says the stolen data came mainly from Orange's Romanian branch. According to him, 380,000 unique email addresses, source code, invoices, contracts, customer and employee information have been exposed.
See also: Australia: Genea suffered a security breach
Rey told BleepingComputer that the breach was not carried out by the HellCat ransomware, but that he had access to Orange's systems for more than a month. On Sunday morning, the data extraction reportedly began. The activity lasted for about three hours without the company detecting it.
Some samples shared with BleepingComputer show email addresses from former and current employees, partners, and contractors of Orange Romania. There is also some information about payment cards belonging to Romanian customers.
According to BleepingComputer, some of the data was quite old (e.g. email addresses from more than five years ago). Also, some of the exposed payment cards had expired. The leak also contains email addresses and customer names of Yoxo, Orange's subscription service.
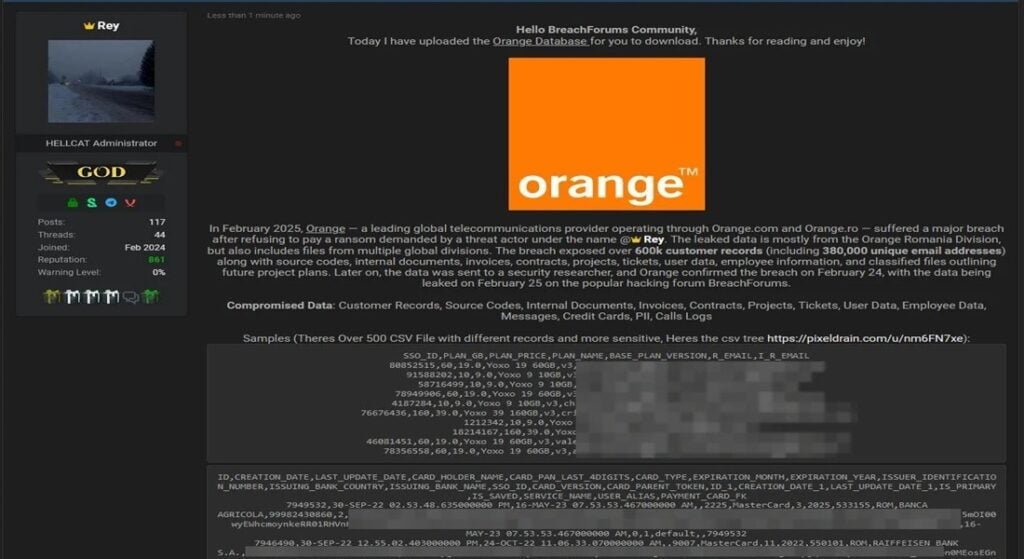
Rey says he stole nearly 12,000 files totaling 6.5GB in sizeafter breaching Orange's systems through compromised credentials and vulnerabilities in the company's Jira software.
See also: Finastra notifies those affected by recent breach
Despite informing and blackmailing the company, Orange chose not to enter into negotiations.
An Orange spokesperson confirmed that the Romanian operation had been the target of a cyberattack.
“We took immediate action and our top priority remains protecting the data and interests of our employees, customers and partners. There was no impact on customer operations and the breach was found to have occurred in a non-critical back office application.“.
“We are committed to providing regular updates. Furthermore, we are committed to complying with all legal obligations related to such incidents and are cooperating with the relevant authorities to address this issue,” the company added.
In recent years, the number of cyberattacks targeting large companies has been increasing. These attacks not only pose a threat to user privacy and organizational integrity, but also have significant financial implications for the affected companies.
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
See also: Hacker pleads guilty to SEC X account breach
One of the main factors fueling this increase in cyberattacks is the growing reliance on digital technologies across various industries. As more and more businesses move towards online operations, they become vulnerable to potential breaches and data theft.
Furthermore, with the advancement of technology, hackers have also become more sophisticated, a fact that makes it easier for them to breach even high-security systems.
Source: www.bleepingcomputer.com
