

The website of Barcelona's tram services , a central element of Spain 's transport network , has reportedly been the target of a Distributed Denial of Service (DDoS) cyberattack. The pro-Russian hacker group calling itself " NoName ", in collaboration with the Cyber Army of Russia , has claimed responsibility for the cyberattack
See also: CatDDoS botnet: Increased infections to carry out DDoS attacks
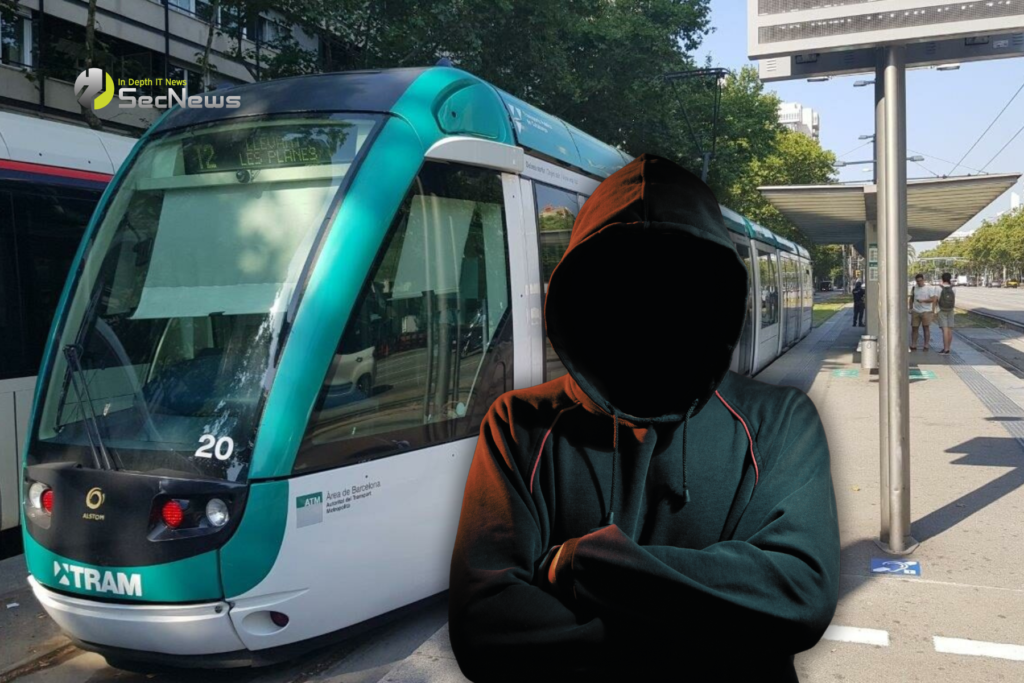
In a post, the group, which claims to be "NoName057(16)", made the announcement which read: "Supporting the attack of our friends from the People's Cyber Army, we are taking down one of Spain's transport websites."
Since first emerging in March 2022, the pro-Russian hacker group NoName has been increasingly active, claiming responsibility for a series of cyberattacks targeting government agencies, media outlets, and private companies across Ukraine, the United States, and Europe.
The Barcelona tram service, which was the target of the DDoS attack, dates back to 1872 and is one of the oldest tram systems in Europe. After being discontinued in 1971, the tram was relaunched in 2004 with the new Trambaix and Trambesòs, which have since become a popular mode of transport throughout the Catalonia region of Spain.
See also: Authorities seize platform selling DDoS services

The details of the Barcelona tram DDoS cyberattack, including possible data breaches and the attackers’ motives, have not been fully revealed. The hacker group announced the attack on May 29, 2024 , and the website is still down as of this writing. The company has yet to acknowledge the incident or issue any official statement regarding the status of its website and services.
The alleged cyberattack on the Barcelona tram highlights the persistent threat to critical entities such as banks and government agencies. However, the absence of an official statement raises questions about the seriousness and credibility of the NoName cyberattack claim.
See also: US public sector: New guide to DDoS attacks
A Distributed Denial of Service (DDoS) attack, such as the one on the Barcelona tram service, is a malicious attempt to disrupt the normal traffic of a targeted server, service, or network by overwhelming it with a “flood” of Internet. This attack leverages multiple compromised systems as traffic sources, often using botnets to amplify the attack. The goal is to make the targeted resource unavailable to users by exhausting its bandwidth, memory, or computing resources. DDoS attacks can cause significant downtime, financial losses, and damage to business reputation, making it critical for organizations to implement robust security measures and response strategies.
Source: thecyberexpress
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
