

The Hive ransomware operation's Tor payment and data-leakage websites were seized as part of an international law enforcement operation after the FBI infiltrated the gang's infrastructure last July.

See also: Yandex denies hack, says former employee leaked source code
The US Department of Justice and Europol revealed today that in July 2022, a covert international law enforcement operation infiltrated the infrastructure of the Hive ransomware gang for about half a year before it was finally exposed.
Through this effort, they were able to predict threats before they occurred and alert potential victims. Additionally, by providing decryption keys to those affected, they saved approximately $130 million that would have otherwise been paid in ransom.
In a warrant request, the FBI revealed that it gained access to two dedicated servers and a virtual private server hosted in California that were leased with email addresses associated with Hive members.
In a joint operation, Dutch law enforcement authorities gained access to two backup servers located within the Netherlands.
Leveraging this access, law enforcement confirmed that these servers served as the primary source of data leakage for the business and were used for negotiations and online boards by operators and partners.
See also: Zacks Investment Research data breach affects 820,000 clients
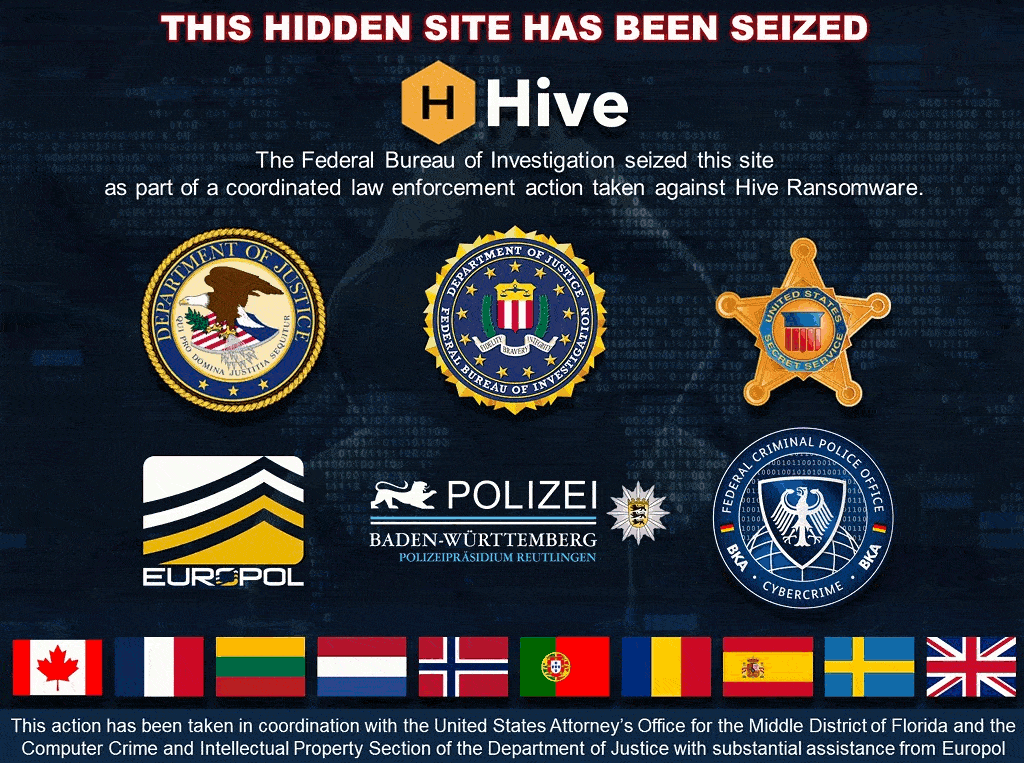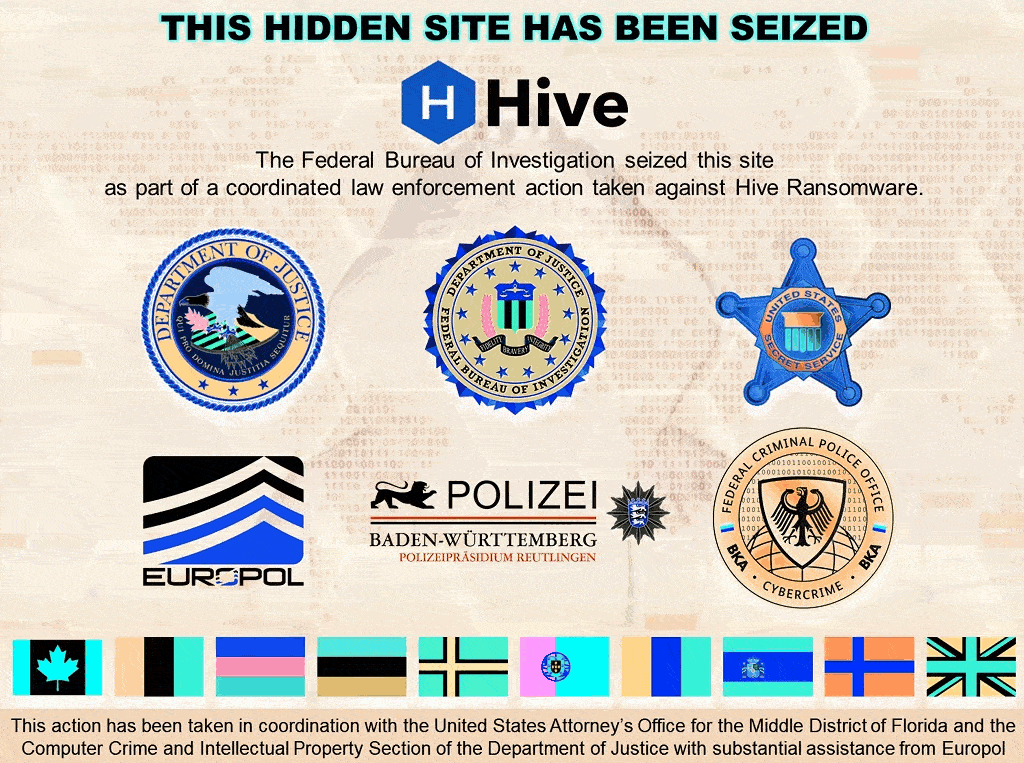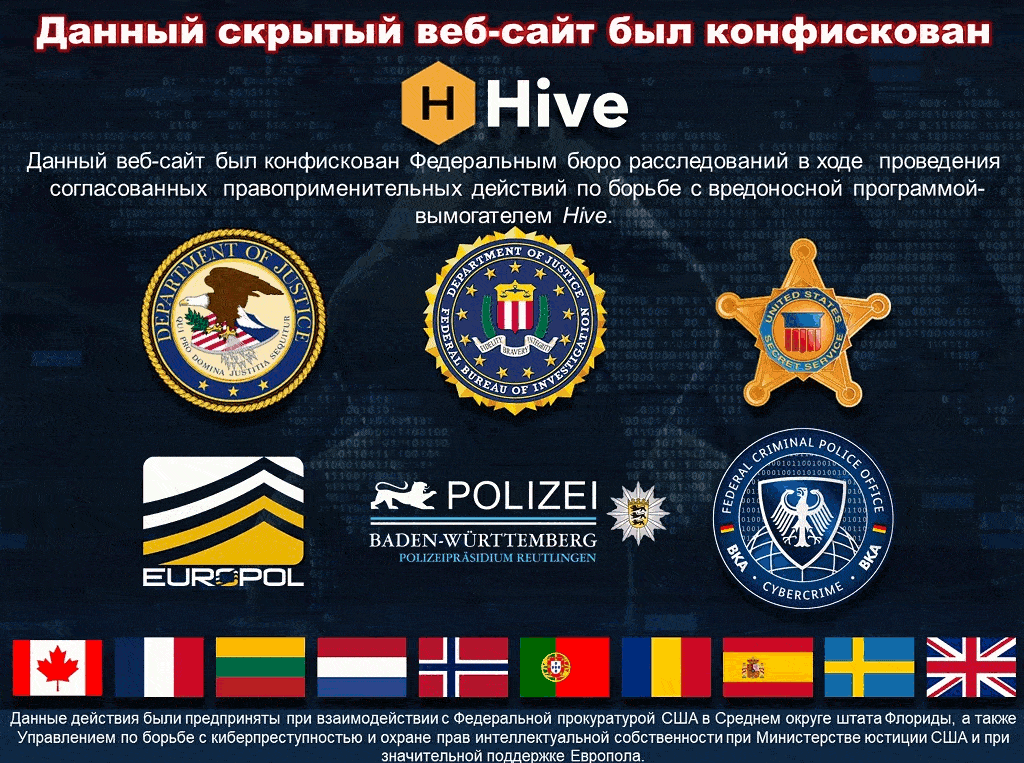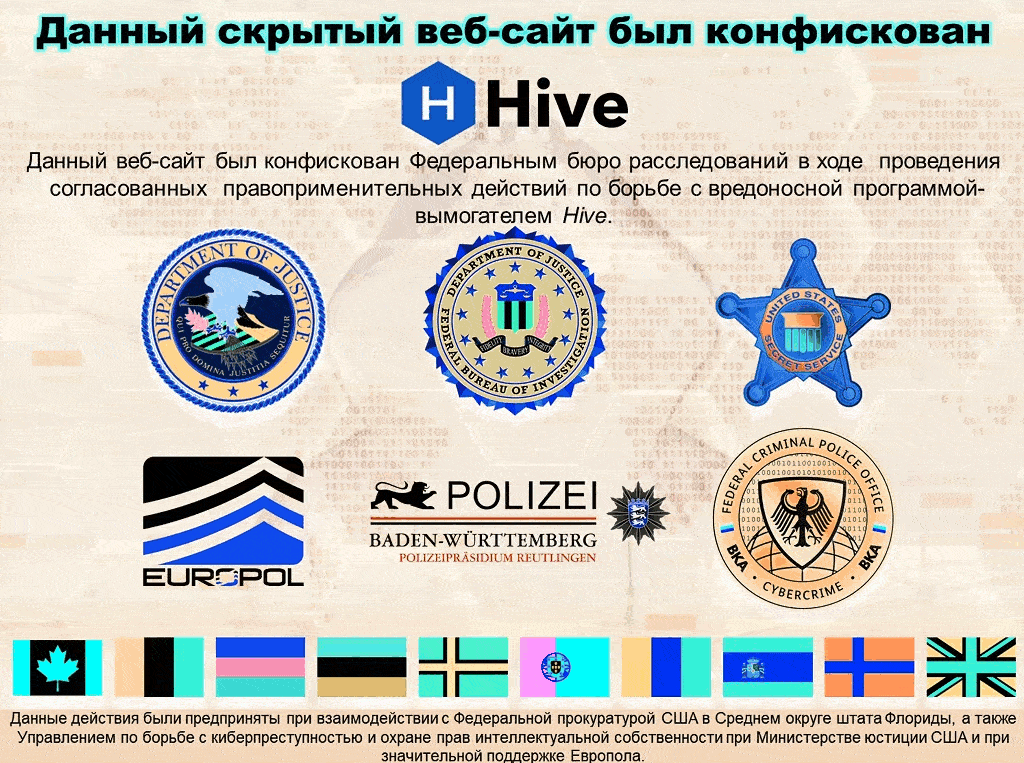
The ransomware gang's Tor websites now display a seizure notice that includes a wide range of other countries involved in the law enforcement operation, including Germany, Canada, France, Lithuania, the Netherlands, Norway, Portugal ,Romania, Spain, Sweden, and the United Kingdom.
Unlike traditional seizure notices used by law enforcement, this image is an animated GIF that alternates between a message in English and Russian, warning other ransomware groups.
Who is behind the infamous Hive ransomware?
The infamous Hive gang has been running as a ransomware-as-a-service (RaaS) since June 2021. This notorious organization is known to infiltrate organizations via phishing emails , exploiting vulnerabilities in publicly exposed devices, as well as using stolen credentials.
Once hackers gain access to the corporate network, they quickly and silently move to other devices while stealing unencrypted data. Their ultimate goal: a double-blackmail attack targeting victims .
When malicious actors gain administrative access to a Windows domain controller, they deploy the insidious ransomware across the entire network to encrypt every connected device.
See also: CISA: Cyberattacks exploit legitimate remote monitoring software
Unlike many ransomware operations that claim to avoid hitting healthcare and emergency services, Hive shows no restraint when it comes to targets.
The ransomware group has caused massive damage with its attacks, leaving behind victims such as Memorial Health System, MediaMarkt, Bell Technical Solutions (BTS), and the New York Racing Association. The latest victim of this malicious organization is Tata Power.
Information source: bleepingcomputer.com
