Twitter revealed yesterday that someone exploited official API 's company (Application Programming Interface) to be able to match phone numbers with the usernames of users of the platform.
Twitter was notified of the security incident by a report published by TechCrunch . According to the report, the API exploit occurred on December 24, 2019. According to the report, researcher security abused Twitter's official API to match 17 million phone numbers with public usernames.
Twitter says that as soon as it learned of the incident, it took action and immediately shut down a large network of fake accounts that were being used for this purpose.
The social networking platform also revealed that it conducted another investigation and discovered that there were others who exploited the API, in addition to the security researcher reported by TechCrunch.
Twitter did not specify who abused the API, but stated that some of the IP addresses used in the API exploitation attempts were associated with state-sponsored hacking groups (either government agencies or hacking groups simply supported by governments).
The Twitter API bug that hackers
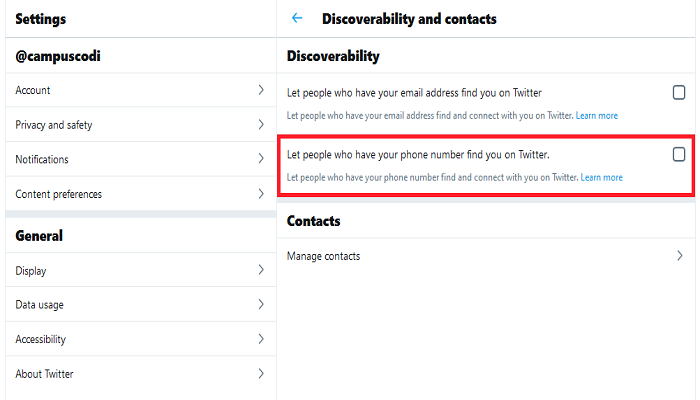
According to Twitter, the attackers exploited a legitimate API endpoint that allows new account holders to find people on the social networking platform . The API endpoint allows users to submit phone numbers and have them matched with accounts.
According to the platform, not all users were affected, but only those who had selected settings the phone number matching option
"People who do not have this setting enabled or do not have a phone number associated with their account were not affected by this vulnerability," Twitter said.
The platform stated that it immediately fixed the bug by making a series of changes to this endpoint so that no other users were affected.