

 According to a new revelation, some hackers are exploiting a legitimate RDP service and using fileless techniques to deploy various malicious payloads (from ransomware to cryptocurrency miners).
Remote Desktop is often used by cybercriminals to carry out attacks.
Remote Desktop Server Abuse
According to Bitdefender, hackers exploit Windows Remote Desktop Server and install a malicious component on the victim's system, called worker.exe , which can be executed via explorer.exe or cmd.exe.
Worker.exe can allow the execution of a series of commands that include the collection of various information system : architecture details, CPU model, kernel, RAM size, Windows version. It also allows the capture of screenshots, the collection of the victim's IP address, domain , and other browser information .
Development of malicious payloads
After hackers collect the above information about the victims' machines, they decide what kind of malicious payload to deploy. For example, if it is a corporate network, then they will likely choose to attack with ransomware.
Researchers discovered that various malicious payloads: clipboard stealer payloads, cryptocurrency miners, ransomware miner payloads, and AZORult payloads.
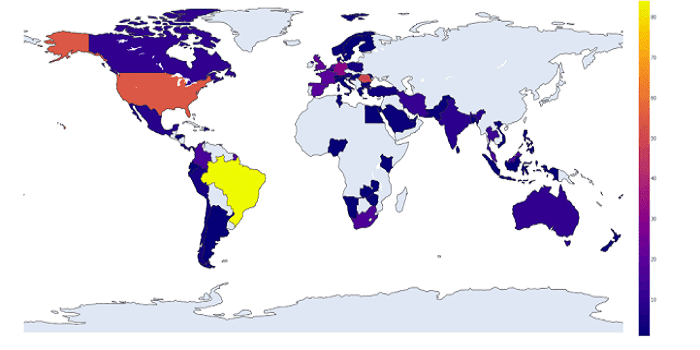
According to researchers, the hacking campaign is targeting victims all over the world. However, most of the victims are from Brazil, the United States, and Romania. Also, the hackers are not targeting specific industries but are trying to attack as many victims as possible.
One of the most common types of payloads in this campaignis miners. “Miners have been in use since April 2018 and earlier, but a wide variety of tools have been used since then, especially in the first months of 2019,” the researchers said.
