

Nemty ransomware: New ransomware was detected over the weekend, with references to the Russian president and an antivirus software program.
It was named Nemty because of the extension it provides to data records after they are encrypted.

Like all malware , Nemty will delete shadow copies for the data records it processes, depriving the victim of the ability to get better versions of the information generated by the Windows.
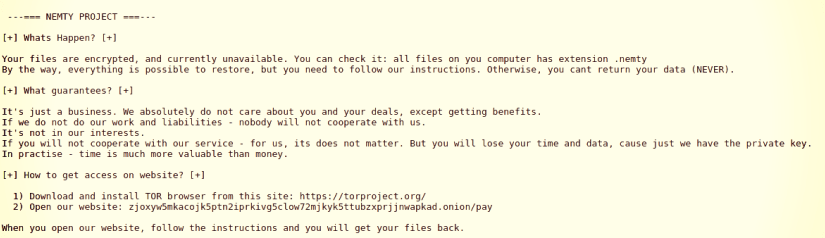
Victims will see a ransom informing them that the hackers hold the decryption key and that they must pay if they want their files back.
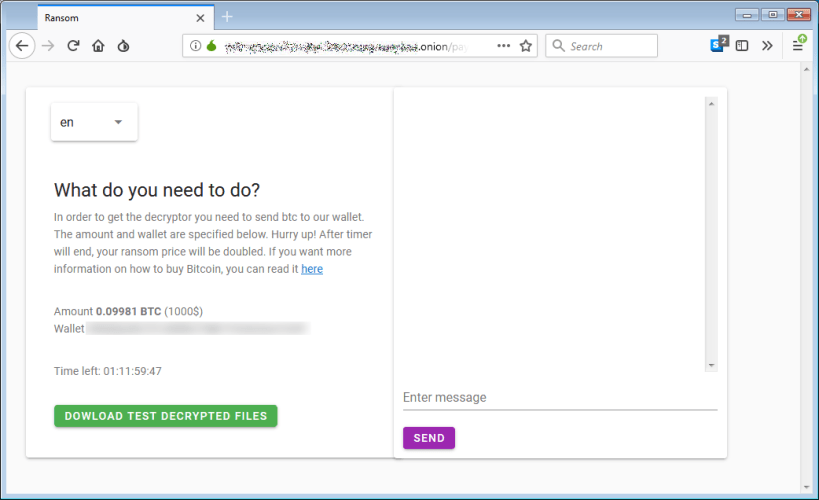
According to BleepingComputer estimates , initially, the ransom demanded was zero.09981 BTC, which has now reached $1,000.
The payment gateway is hosted on Tor for anonymity and customers must add configuration file . A hyperlink is then provided to a different website that features the chat feature and additional call data.
Messages within the code
Security researcher Vitali Kremez took a closer look at the malware and saw that it comes with an unusual identifier for the mutex object. The creator is called “hate,” as shown in the image below.
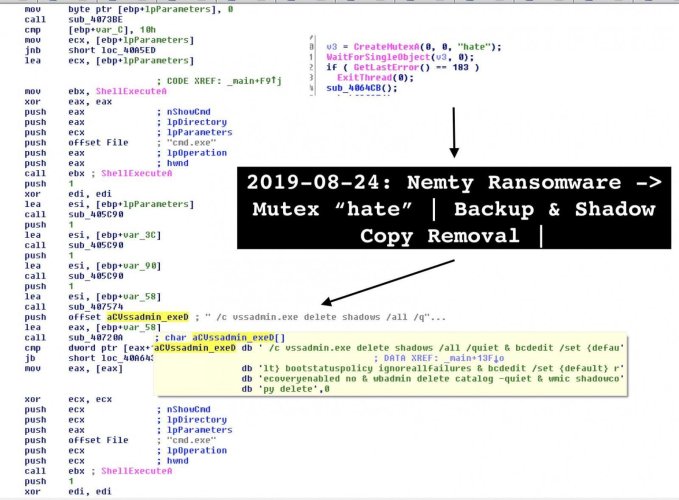
A single object (mutex) allows applications to set elements by providing access to them to at least one execution thread at a time.
Another strange factor observed in Nemty's code is a hyperlink to an image of Vladimir Putin, with a caption saying: "I added you to the record of [insult], however solely with pencil for now."
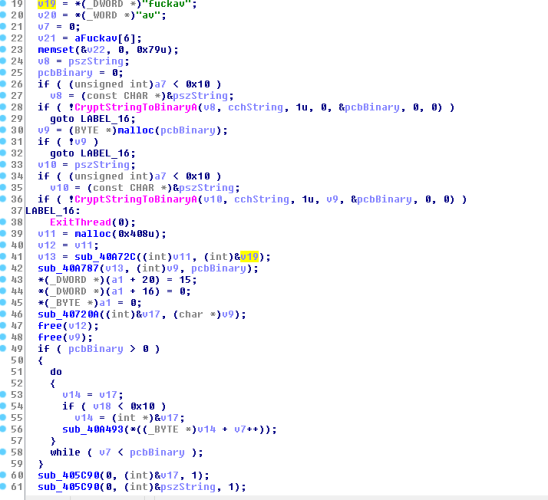
Additionally, the mention of antivirus is also striking. At first, a strange factor appeared in the code, which, upon second glance, is used to decode base64 strings and create URLs.
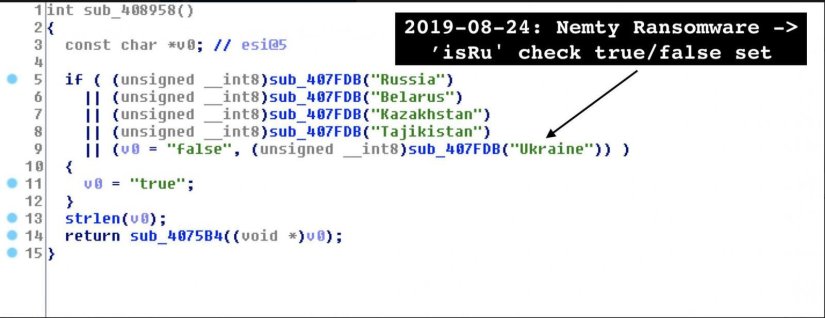
Another factor that attracts attention is the verification that Nemty carries out for the creation of IT systems in Russia, Belarus, Kazakhstan, Tajikistan and Ukraine.
The “isRU” within the malware code simply signals the techniques located in one of 5 international locations and then sends the hacker the computer identifier, username, operating system, and computer ID.
It is unclear how Nemty is distributed, but sources say hackers operate via compromised remote desktop connections (RDP).
Compared to phishing e-mail, which is currently the most common distribution technique, leveraging an RDP connection gives the attacker direct access and control.
