

A new ransomware called CommonRansom has been discovered that has a rather strange way of working. In order to decrypt the computer's files, after the user pays the requested amount, they must also activate remote desktop services and provide the details of an administrator account on the computer. CommonRansom was discovered by Michael Gillespie after one of his victims registered the new ransomware with his service, ID Ransomware.
When this ransomware infects a computer, it converts the format of every file (.txt .doc .exe and many more) to .CommonRansom. It also creates a new text file in all folders called DECRYPTING.txt, which displays the following message.
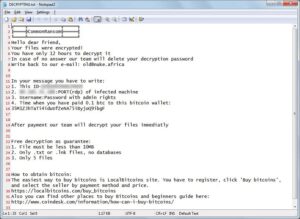
In this strange message, the creator of CommonRansom asks his victims to pay 0.1 BTC and send an email with the following information:
This ID-[VICTIM_ID][IP_ADDRESS]:PORT(rdp) of infected machineUsername: Password with admin rightsTime when you have paid 0.1 btc to this bitcoin wallet:
35M1ZJhTaTi4iduUfZeNA75iByjoQ9ibgF
Under no circumstances should anyone give these details to anyone, as once the attacker logs in, there is no way for the computer owner to see what they are doing. They can decrypt the files and log out, but at the same time they can install additional malware and other malicious programs, or even steal sensitive data.
While no sample of the ransomware, from the ransom note we know of a Bitcoin address that appears to have had some activity in the past.
