

Google security researchers have removed 22 Android apps infected with the HiddnAd and Guerilla adware.

They were recently discovered after a Sophos investigation last week and there is no connection between them as each one works in a different way. Let's take a closer look at them
The first adware discovered was Guerilla, which Sophos researcher Chen Yu found in 15 apps on the Play Store, most of which were clones of well-known successful apps. All of the apps were fully functional but also came with the adware hidden in their code.
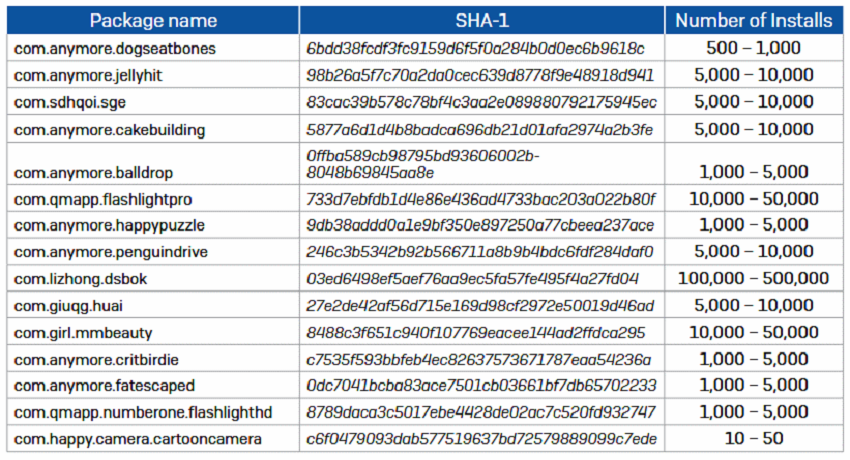
Yu calls it malware, saying the malicious code it contained acted as a backdoor, allowing the app to download and run any additional component. The malicious users could have downloaded anything they wanted, but they focused on ad-clicking plugins that generated revenue for them. “This is done stealthily, so the app user may not even notice this behavior,” Yu wrote in a report he released. “The ad-clicker is resource-hungry and annoying, but the real danger of Guerilla is its ability to download anything else it wants because of the backdoor code it contains.”
The second adware is HiddnAd which was hidden behind 7 applications (6 QR code readers, 1 smart compass), all of which were available through the Play Store.
HiddnAd was not as sophisticated as Guerilla, and instead of opening a backdoor on devices to download whatever extras they wanted, the crooks hid the adware's malicious code inside an image element. Apps infected with HiddnAd passed Google's security checks because they delayed the execution of any malicious code for six hours, bypassing many of the Play Store's security scans.
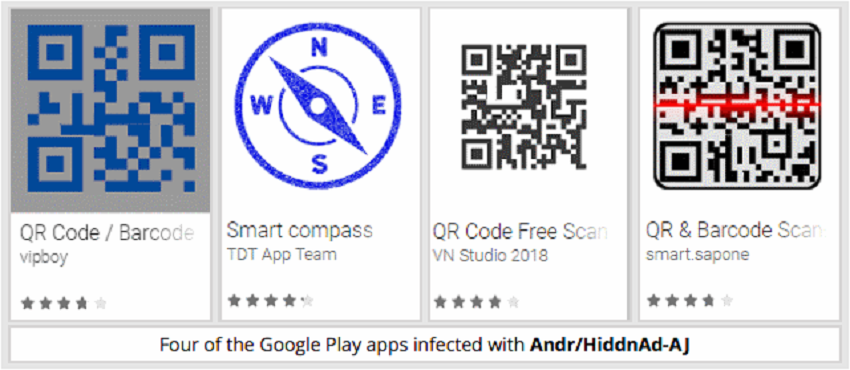
Unfortunately, Sophos did not release a full list of applications that contained the HiddnAd adware, only listing 4 of them.
