

Oxygen router? Since it is one of the first articles in the Pentesting , it would be better if I explained what it is. Penetration testing is used to assess security and find security gaps by simulating attacks that a hacker could make to harm you. The pentester uses almost the same tools that a hacker uses and the most important thing is that he knows how he thinks! A good example of pentesting is the authentication attack, which I will show you below…

Before I show you how I bypassed the authentication of Oxygen , which is actually used in corporate connections by a large Greek company, we will make an introduction....
Basic access authentication is the method by which HTTP transfers the username and password when we make a request. It is the simplest method to transfer sensitive information. There is no need for Cookies, Sessions or login forms. The information is encoded with base64 but is not encrypted!
Client
When we send our data with Basic authentication then:
- The username and password are combined as follows username:password
- The string combination is done as follows base64(username:password)
QWxhZGRpbjpvcGVuIHNlc2FtZQ==
- Authorization is basic
Authorization: Basic
But too much theory will destroy our project.
Step 1
I want to log in to the Router but there is a problem. I don't know the username and password 🙂
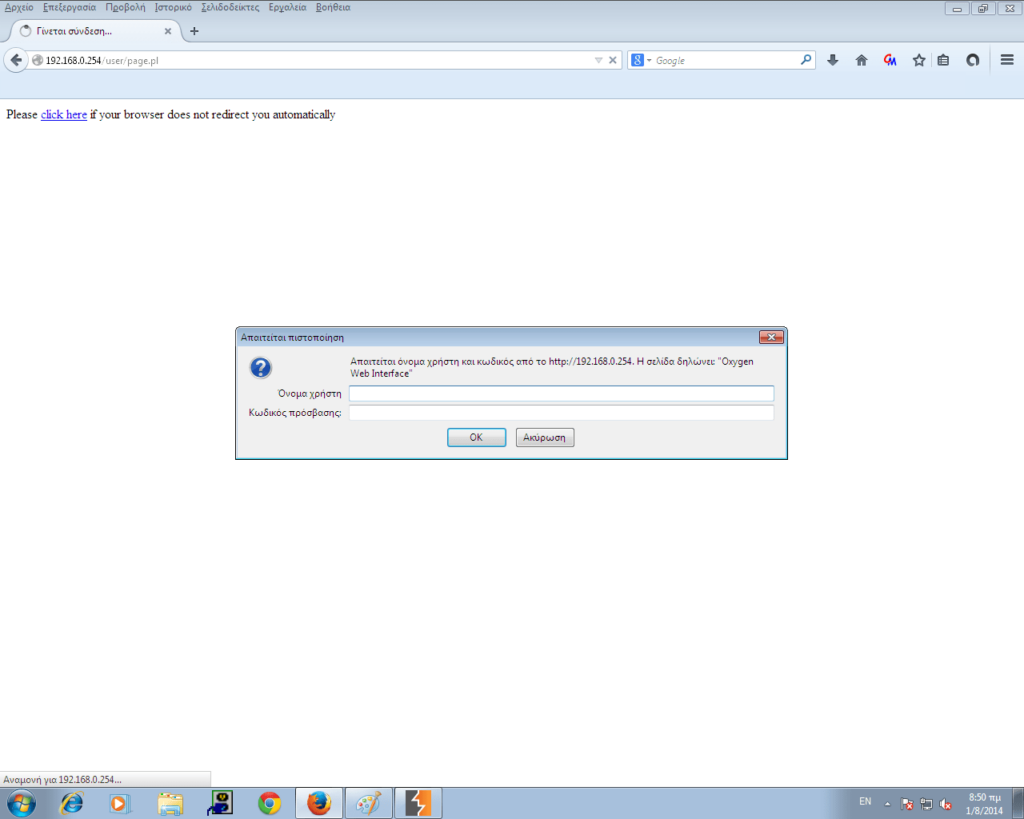
Step 2
I randomly try admin(username) with 1234 (pass)
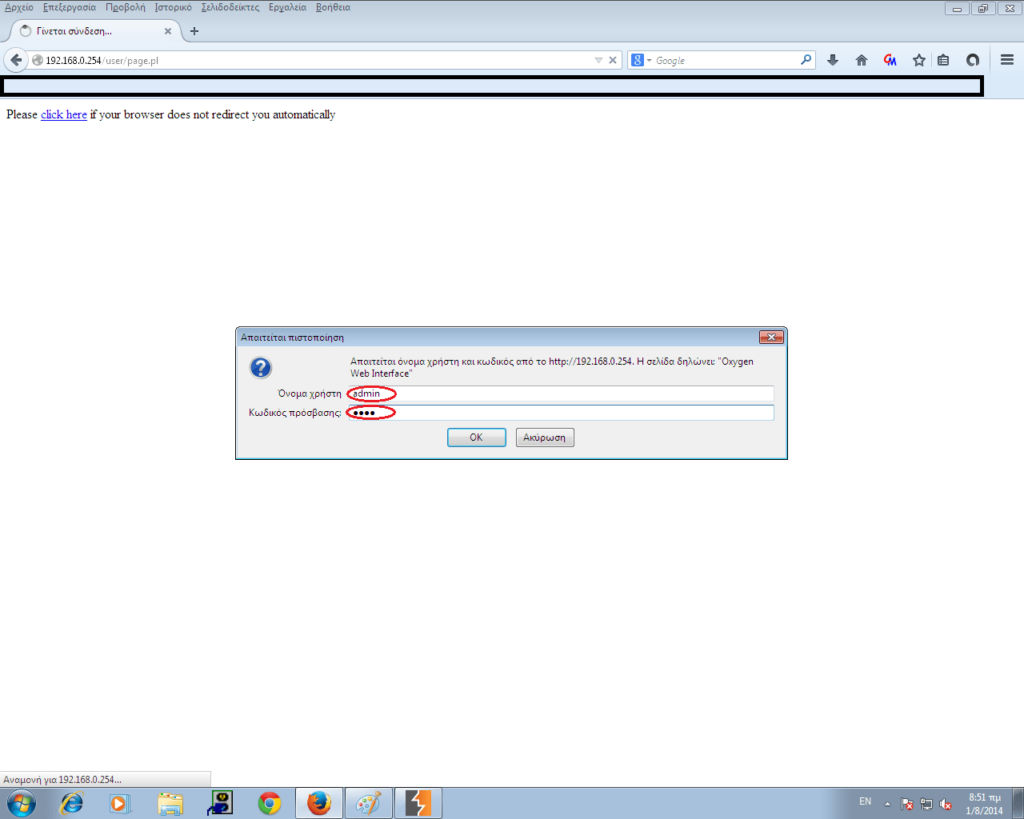
Step 3
The username and password have been encoded in base64 as I explained above.
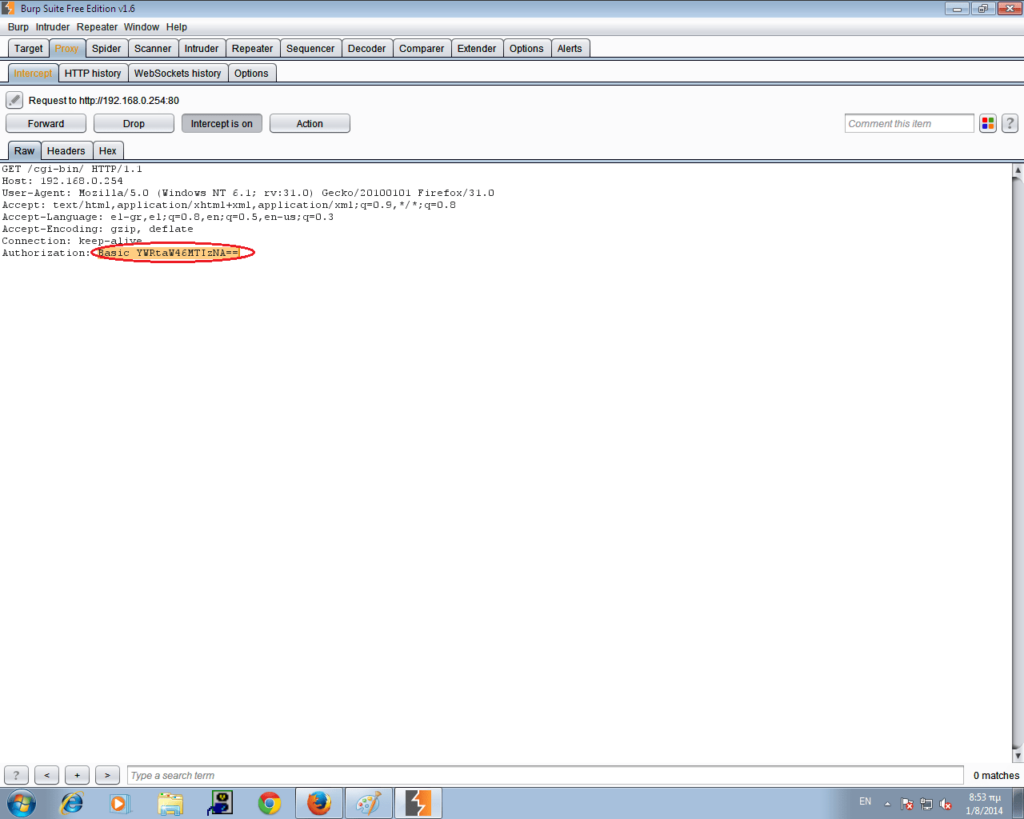
Step 4
I decode them to see my data in plaintext.
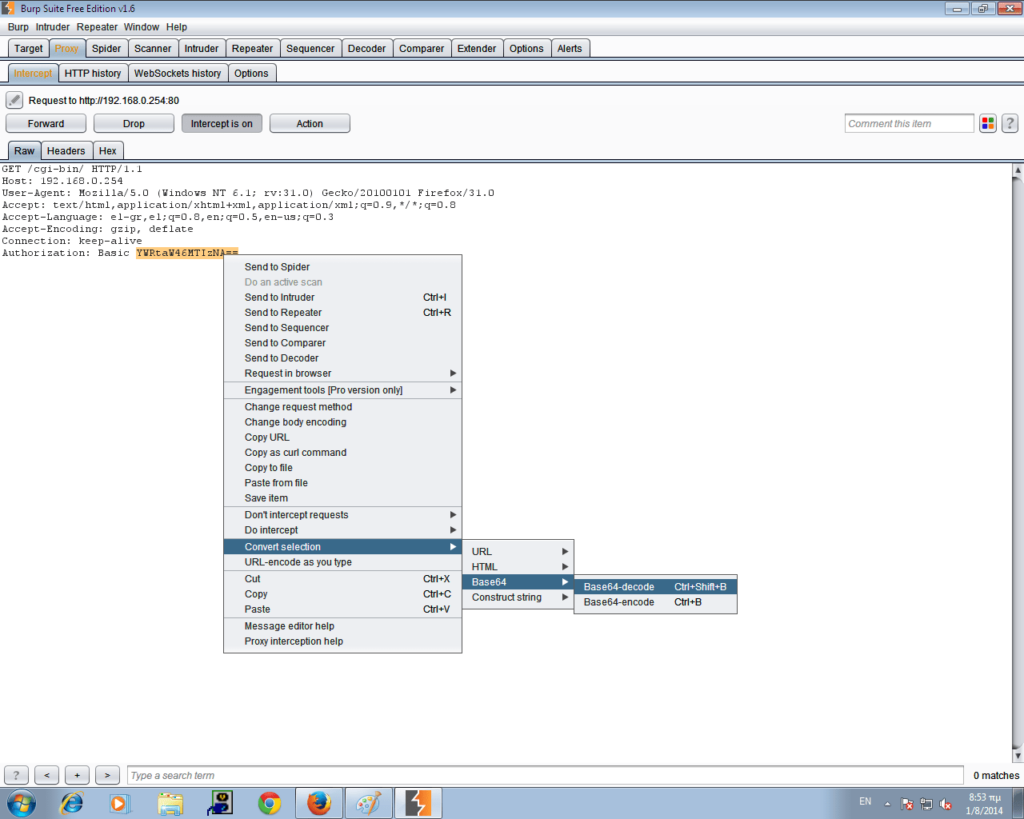
Step 5
The truth is that there were other steps before, but for obvious reasons I won't write them down 🙂
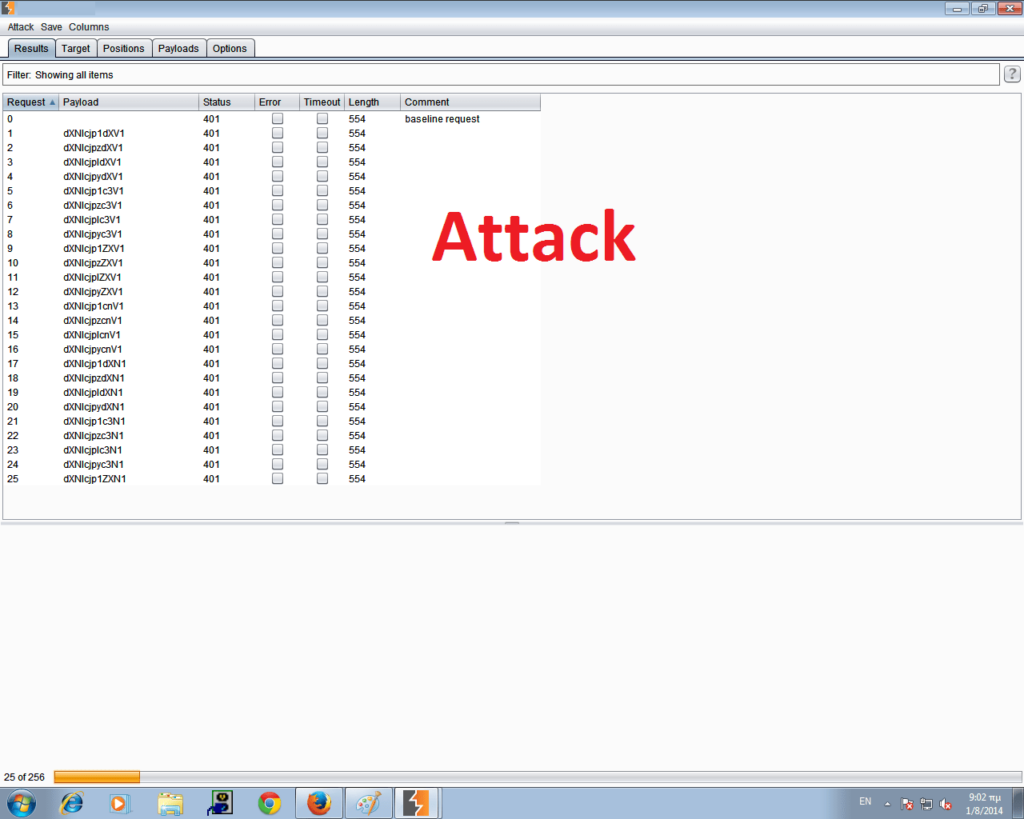
Step 6
Game Over!!!
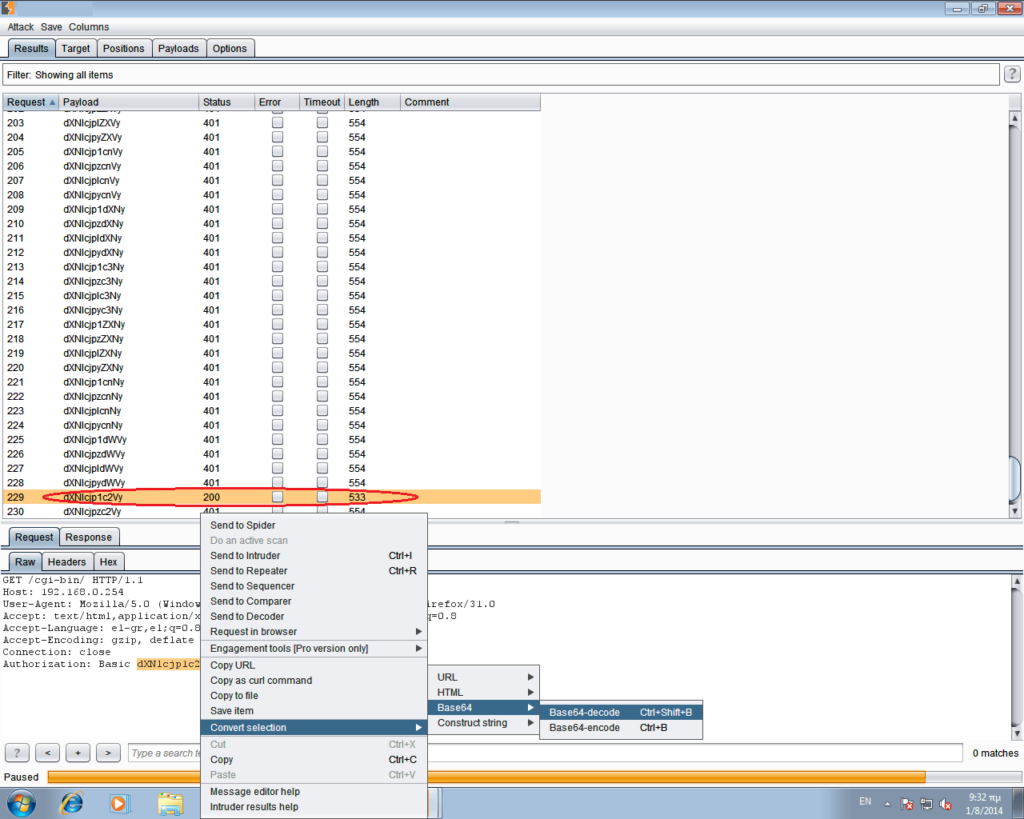

This particular attack is the easiest since authorization is basic. The award goes entirely to the hacker.Developers place more importance on their code being functional than secure!
I will also occasionally present some posts on my blog Pentest Library.
Food for the mind
- https://en.wikipedia.org/wiki/Basic_access_authentication
- https://www.ietf.org/rfc/rfc2617.txt
