

 In September, emails about people in Africa suffering from Ebola and unusual invitations to a World Health Organization (WHO) conference were detected. The goal of the emails was, as usual, to trick recipients into stealing money after they engaged in a conversation with the senders of the messages.
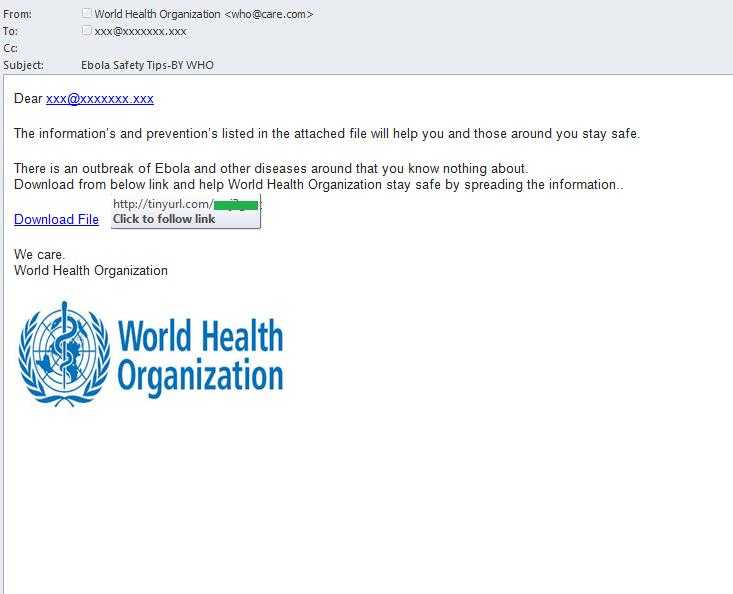
In October, it was the turn of cybercriminals, who used the news surrounding the Ebola virus to send out emails containing malware. Once again, the WHO appeared to be the sender of the messages, which is not surprising, as this is the organization that deals with various diseases and epidemics on a global level.
In the text of the detected messages, the criminals tried to convince the recipients that the WHO has prepared a file with general information and safety measures that will help protect the users and those around them from the deadly virus and other diseases. Furthermore, the recipient was asked to distribute this information to help the WHO.
To disguise the real link, a link shortening service was used, which directed users to a popular cloud storage service. There, the criminals had stored the malware, Backdoor.Win32.DarkKomet.dtzn, disguised as a document from the WHO. This malware is designed to steal personal data. We note that access to the file was blocked quite quickly by the service administrators, and, most likely, for this reason, the criminals decided to change their letter. The next day, a similar announcement was released allegedly from the WHO, this time with the same malware in the message itself.

Cybercriminals rarely miss such opportunities and exploit current events and names of famous organizations to trick spam recipients.
