

Users of popular open source libraries "colors" and "faker" were surprised after seeing their apps using these libraries print unusual data and crash.

See also: NPM identified and fixed many security flaws
Some assumed that the NPM libraries had been compromised, but it turns out that this is all a very long story.
The developer of these libraries intentionally introduced an infinite loop that created an issue in thousands of projects that depend on the "colors" and "faker" libs.
The colors library receives over 20 million weekly downloads on npm alone and has nearly 19,000 projects that rely on it. Meanwhile, faker receives over 2.8 million weekly downloads on npm and has over 2,500 dependents.
Open source revolution?
The developer behind the popular open source NPM libraries “colors” (also known as Colors.js on GitHub) and “faker” (also known as “faker.js” on GitHub) intentionally introduced rogue commits into them that affect thousands of applications that rely on these libraries.
See also: GitHub finds 7 code execution vulnerabilities in 'tar' and npm CLI
Yesterday, users of popular open source projects such as Cloud Development Kit (aws-cdk) were surprised to see their applications printing nonsense messages to their console.
These messages included the text “LIBERTY LIBERTY LIBERTY” followed by a sequence of non-ASCII characters:
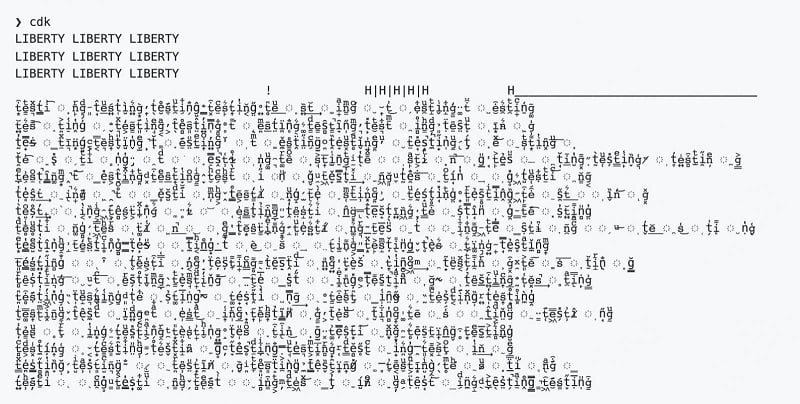
Initially, users suspected that the 'colors' and 'faker' libraries used by these projects had been compromised, since they resembled the way the coa, rc, and ua-parser-js libraries were compromised by malicious actors last year.
But, in reality, it was the developer behind colors and faker who appears to have intentionally committed the code responsible for the major blunder.
The developer, named Marak Squires, added a “new American flag module” to the color.js library yesterday in version v1.4.44-liberty-2 which he then pushed to GitHub and npm.
The continuous loop introduced in the code will continue to run indefinitely, endlessly printing the unusual sequence of non-ASCII characters to the console for any applications that use “colors”.
See also: Are you using PAC files? Beware of the NPM package error
Similarly, a compromised version '6.6.6' of faker was published on GitHub and npm.
The reason behind this evil on the developer's part seems to be retaliation against large corporations and commercial consumers of open source projects that rely heavily on free and community-supported software, but do not, according to the developer, give anything back to the community.
In November 2020, Marak had warned that he would no longer support large companies with his "free work" and that commercial entities should consider either splitting the projects or compensating the developer with an annual "six-figure" salary.
Marak's bold move opened a can of worms and attracted mixed reactions.
Some members of the open source software community praised the developer's actions, while others are horrified by it.
GitHub has reportedly suspended the developer's account. Of course, this has also caused mixed reactions.
In the meantime, users of the "colors" and "faker" NPM projects should ensure they are not using an insecure version. Downgrading to an older version of color (e.g. 1.4.0) and faker (e.g. 5.5.3) is a workaround.
Information source: bleepingcomputer.com
