

German software company SAP has released its May 2020 security updates, which fix six critical vulnerabilities found in many of its products. Of these vulnerabilities, three have a severity rating very close to the maximum. In addition, all but one of these vulnerabilities can be exploited remotely, do not require user interaction, and have a low attack. Some of them are new, while others are not. In particular, one of them is an update to a security issue from April 2018. Furthermore, these vulnerabilities differ from the security issues the company announced a few days ago, which affect cloud-based products and will be fixed before the end of the second quarter of 2020. SAP's May 2020 Security Update Day includes several alerts for various types of vulnerabilities, with half of them being critical.
The most critical of these is identified as CVE-2020-6262 and has a severity rating of 9.9 out of 10. It is a code in Data Retrieval and affects multiple versions of SAP Application Server ABAP (2008_1_46C, 2008_1_620, 2008_1_640, 2008_1_700, 2008_1_710, 740). The second most serious security flaw is identified as CVE-2020-6242, with a severity rating of 9.8 out of 10. It is a missing authentication check in SAP Business Objects Business Intelligence Platform, versions 1.0, 2.0, and 2.X. A security update for the Chromium browser that ships with the SAP Business client is also listed as critical, with a rating of 9.8 out of 10, based on version 3 of the Common Vulnerability Scoring System (CVSS). Another code injection vulnerability was addressed in the backup server of SAP Adaptive Server Enterprise (ASE) version 16.0. The severity of this flaw, identified as CVE-2020-6248, is rated 9.1 out of 10. An information disclosure flaw, identified as CVE-2020-6252 and rated 9 out of 10, in SAP ASE's graphics management tool, Cockpit, is the latest in a list of critical vulnerabilities the company is addressing with this week's updates.
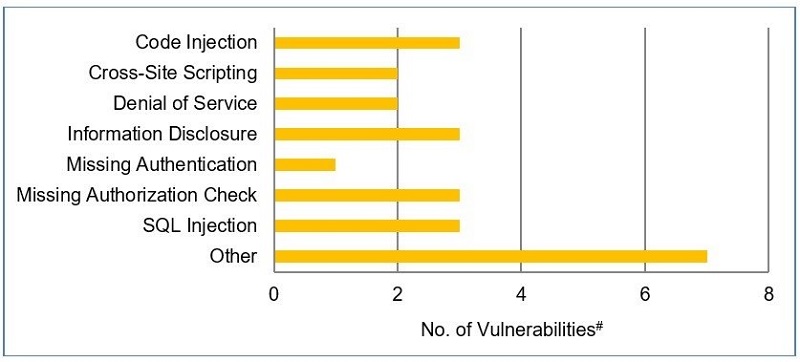
SAP also addressed other high and medium severity security flaws, which affect Adaptive Server Enterprise and some of its components:
- A SQL injection flaw, identified as CVE-2020-6241, has a severity rating of 8.8 out of 10.
- A code injection in the SAP ASE XP server on the Windows, identified as CVE-2020-6243, with a rating of 8 out of 10.
- An SQL injection affecting Web Services, identified as CVE-2020-6253 and rated 7.2.
- Information disclosure, identified as CVE-2020-6250, with a rating of 6.8.
- Lack of authorization checking, identified as CVE-2020-6259, with a rating of 6.5 out of 10.
SAP customers are advised to receive this month's security updates, which are available on the company's support portal
