

Citrix has fixed three vulnerabilities found in multiple versions of ShareFile storage zone controllers that could allow hackers to gain access to the company's customer files. ShareFile is a service designed for businessesthat need a content collaboration, file sharing, and synchronization system. Data is accessed from internal or cloud storage zones and is transferred to the user in a secure manner through a storage zone controller.
Thousands of servers were exposed due to the bugs found in the company. Specifically, the three security bugs, identified as CVE-2020-7473, CVE-2020-8982 and CVE-2020-8983, affect the base versions of ShareFile's storage zone controllers (5.9.0, 5.8.0, 5.7.0, 5.6.0 and 5.5.0), while their intermediate versions (5.9.1 / 5.8.1 / 5.7.1 / 5.6.1 / 5.5.1) are not affected. However, the company states in a related announcement that storage zones created using a vulnerable version of the storage zone controller are at risk even if the controller has been updated.
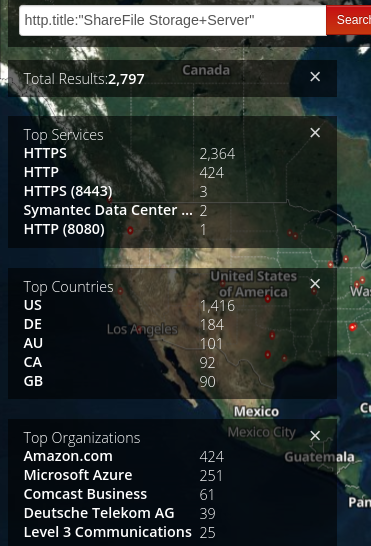
Nate Warfield, a senior security program manager at the Microsoft (MSRC), searched for exposed Citrix ShareFile storage servers on Shodan and found about 2,800. There are no clear details about the security flaws in question, but Warfield noted that they are quite significant, so fixing the servers should be a priority. Additionally, the lack of technical information means there is still plenty of time before an exploit or other form of attack can be carried out.
Customers with Citrix-managed storage zones do not need to take any specific action. Customers who manage their own zones should ensure they are running a supported version and then use a Citrix mitigation tool . This is a simple tool that checks if a ShareFile server is vulnerable to the flaw identified as CVE-2020-7473 and is available on GitHub from Dimitri van de Giessen , an ethical hacker and systems engineer. De Giessen works for a company that is a Citrix on-premise user and received advance information about the critical security update. This allowed him to track what the update did for the flaw identified as CVE-2020-7473. In a security bulletin, Citrix thanked Danske Bank Red-Team for their cooperation, which resulted in protecting its customers from the other two security flaws.
