

The recent vulnerability in the Joomla CMS led the company Top.Host to disable the admin interface!

As our friend/reader Fotis, administrator of the website RetroComputers.gr , informed us, malfunctions occurred at the well-known Greek company Top.Host .
Specifically, the vulnerability in the well-known CMS Joomla that was made public in recent dayshas created many problems for hosting companies abroad and in Greece.
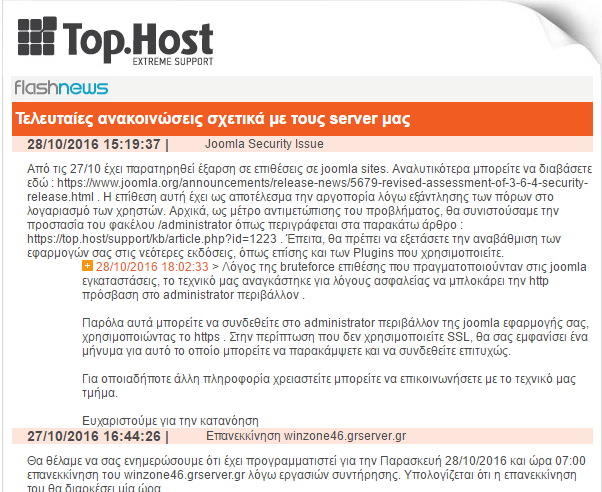
The company announced that their technicians were forced to block http access to the administrator environment of the websites for security reasons. See the announcement below [here]:
It should be noted that Joomla CMS is one of the most widespread in Greece, mainly for company presentation websites or e-shops. Consequently, a large number remain unpatched and with automated tools, websites can be identified and targeted or altered.

From the perspective of Top.Host, it is extremely important that it has informed its customers about the security issue in Joomla CMS, which shows the seriousness with which it deals with such issues. On the other hand, we believe that it should proceed with a massive upgrade of the version of all Unpatched Joomla on its servers, so that even customers who do not have the relevant knowledge are protected. Because some modules may not work after the Update, this can certainly be addressed by the technicians on a case by case basis.
In general, the level of managed service hosting in Greece seems to lag significantly behind its counterparts abroad. Perhaps this is the operating model that hosting companies and related providers should focus on in the near future, in order to provide their Greek customers with high-standard, high-security services combined with a reasonably low cost.
