

In the world of cybersecurity, a new incident has come to add to an already difficult year: a threat actor operating under the alias “888” has allegedly released stolen data belonging to LG Electronics. The incident became known on November 16, 2025, causing great concern, as it includes critical material.
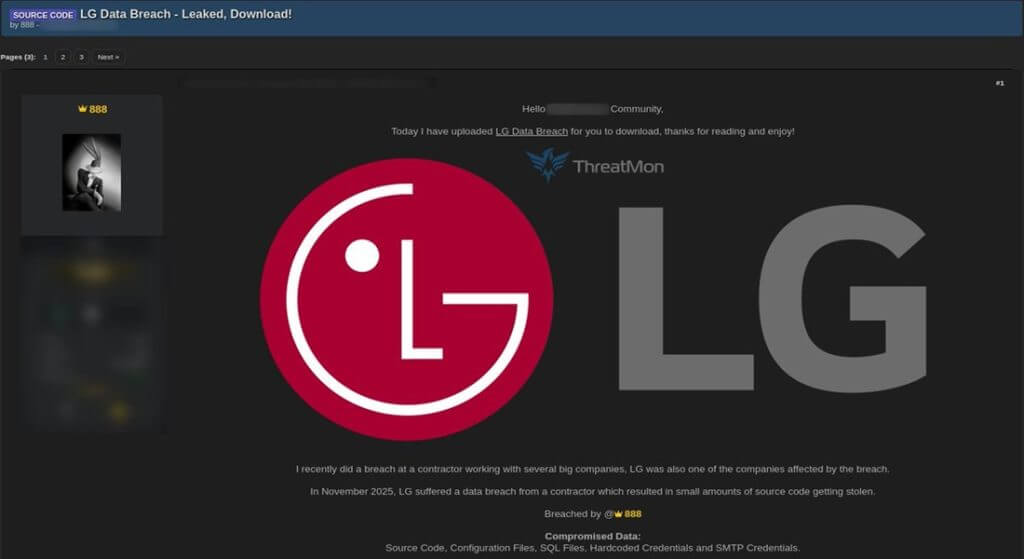
According to existing reports, the leaked data includes source code, configuration files, SQL databases , and encrypted credentials. Of particular concern is the disclosure of SMTP server information, which is a key link in LG's internal communications.
The ThreatMon disclosure and potential supply chain vulnerability
The leak was first reported in a post on ThreatMon. "888" reportedly uploaded samples of the data to prove the authenticity of the breach.
See also: The npm registry worm is still out of control
While the incident itself does not appear to have been a direct attack on LG’s systems, reports suggest the hacker gained access through a contractor. This raises the possibility of supply chain vulnerabilities — one of the most dangerous forms of attack, as they often go unnoticed until it’s too late.
Dangerous credentials within the code
The presence of hardcoded credentials in the source code is a practice that experts consider particularly dangerous. Such negligence could allow attackers to impersonate LG personnel or gain access to connected services.
SMTP credentials open the door to targeted campaigns phishing , where cybercriminals can send legitimate-looking emails to mislead LG partners or customers. These types of attacks are among the most effective, as they exploit the trust inherent in a corporate email.
The profile of “888”: A well-known and dangerous perpetrator
"888" is no stranger to cybercrime. Since 2024, it has targeted high-profile organizations such as Microsoft, BMW Hong Kong, Decathlon, and Shell. Its practices include selling data on forums, blackmailing organizations for ransom, and working with initial access brokers.
See also: SpearSpecter: APT42's new cyberespionage campaign
Although no ransom demand has been confirmed in the LG case, published samples show the leakage of sensitive data — something that could undermine the company's intellectual property in products such as smart home devices, televisions, and IoT ecosystems
A year full of cyberattacks for LG
LG Electronics has yet to make an official statement, leaving questions about the extent of the breach. The incident, however, comes on the heels of an already tumultuous year: just in October, the company's telecommunications arm, LG Uplus, confirmed a separate breach that affected customer data.
Security experts estimate that the incidents may be related through common vulnerabilities, such as neglected security updates to cloud services or third-party tools integrated into the company's infrastructure.
The potential consequences for the global IoT market
If the source code of LG devices has indeed been exposed, the damage could extend beyond the company, reaching millions of users worldwide. IoT rely on firmware that, if publicly disclosed, could expose security vulnerabilities, allowing attacks on home networks.
See also: RondoDox exploits vulnerable XWiki servers
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.

Experts warn that such leaks can act as a "hacking guide" for attackers looking for ways to bypass the protection of connected devices.
The importance of immediate response
As the investigation continues, security firms are urging organizations worldwide to routinely scan for exposed credentials and immediately renew access keys that look suspicious. The LG case is a reminder of how vulnerable global supply chains are: a simple oversight at one external partner can escalate into a crisis for the entire organization.
For LG, the challenge now is rapid update, transparency, and remediation — before the consequences of the leak spread even further.
