

A new Android malware called Crocodilus tricks users into providing their crypto wallet seed phrase.
ThreatFabric researchers observed that although Crocodilus is a new banking malware, it has fully developed capabilities for controlling the compromised device, collecting data, and remote control.
According to the research, the malware is distributed via a dropper that bypasses the security protections of Android 13 and later versions . The dropper installs the Crocodilus malware without enabling Play Protect, while also bypassing Accessibility Service restrictions .
See also: New RESURGE malware exploits Ivanti vulnerability
Crocodilus also incorporates social engineering to trick victims into providing their crypto wallet seed phrase. This is accomplished through a screen overlay that warns users to “up back their wallet key in settings within 12 hours.” Failure to do so risks losing access to their wallet, according to the warning.
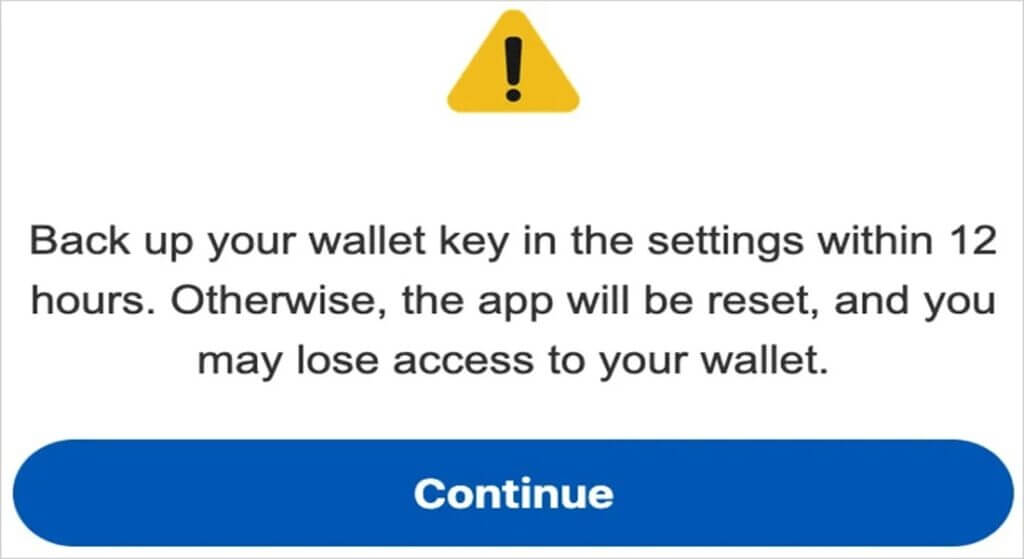
“ This social engineering trick directs the victim to navigate to their seed phrase (wallet key), allowing the Crocodilus malware to collect the text using its Accessibility Logger ,” ThreatFabric explains .
“With this information, attackers can take full control of the wallet and empty it,” the researchers say.
In the first attacks, the Crocodilus malware primarily targeted users in Turkey and Spain. Furthermore, the malware is said to be of Turkish origin.
See also: CoffeeLoader malware: Learn everything about the new threat
It is unclear how the initial infection occurs, but typically, victims are tricked into downloading droppers via malicious websites, fake promotions (on social media or SMS), and third-party app stores.
Upon startup, Crocodilus malware accesses the Accessibility Service to unlock access to screen content, perform navigation gestures, and monitor application launches.
When the victim opens a targeted banking or crypto wallet app, Crocodilus displays a fake page, on top of the real app, to steal the victim's account credentials.
According to the researchers, the bot component of the malware supports a set of 23 commands that it can execute on the device. Some of the most important ones are:
- Activate call forwarding
- Opening a specific application
- Publish a push notification
- Send SMS to all contacts or a specified number
- Receiving SMS messages
- Request for device administrator rights
- Screen blackout
- Lock screen
- Make it the default SMS manager
The malware also offers functionality remote access (RAT), which allows its operators to tap the screen, navigate the user interface, perform swipe gestures, and more.
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
There is also a dedicated RAT command to take screenshots from the Google Authenticator app and obtain one-time passwords.
See also: FBI: Fake document conversion tools spread malware
While performing these actions, Crocodilus malware operators can black out the screen and mute the device to hide the activity from the victim.
Android users are advised to avoid downloading APKs outside of Google Play and ensure that Play Protect is always enabled on their devices. You should always verify the authenticity of an app before installing it. This can be done by checking the developer and user reviews.
The use of reliable security software and regular updates of the operating system and applications are also essential .
Source: www.bleepingcomputer.com
