

The free and open-source decentralized social networking platform Mastodon has fixed four vulnerabilities - one of them is critical.
See also: EYP establishes its own SOC - Cybersecurity Operations Center
Mastodon has about 8.8 million users distributed across 13,000 separate servers (instances) hosted by volunteers to support distinct yet interconnected (federated) communities.
And all four issues discovered by independent auditors of Cure53, a company that provides penetration testing for online services, have been fixed. Following a request from Mozilla, the auditors reviewed the Mastodon code.
The most serious vulnerability, identified as CVE-2023-36460 and called TootRoot, gives attackers an easy way to compromise target servers.
See also: New Big Head ransomware displays fake Windows update notification
CVE-2023-36460 is a vulnerability in Mastodon's media processing code that allows the use of media files in toots (the equivalent of tweets) to cause a range of issues, from denial of service (DoS) to arbitrary remote code execution.
Although Mastodon's security bulletin is brief, security researcher Kevin Beaumont highlighted the risks associated with TootRoot, saying that a “toot” could be used to place backdoors on the servers that deliver content to Mastodon's users.
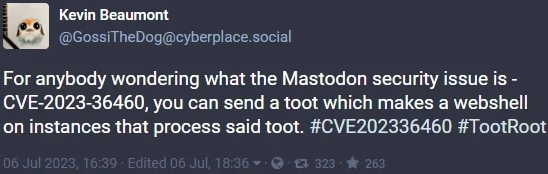
Such a breach would give attackers unlimited control of the server, the data it hosts and manages, and would extend to users' sensitive information.
The second critical severity flaw is CVE-2023-36459, a cross-site scripting (XSS) vulnerability in the oEmbed preview cards used in Mastodon, which allows bypassing HTML sanitization in the target browser.
Attackers who exploit this flaw could use it for account hijacking, user impersonation, or access to sensitive data.
See also: Charming Kitten: Uses the new NokNok malware for macOS
The other two vulnerabilities addressed by Mastodon are CVE-2023-36461, a high-severity DoS bug that can be exploited via slow HTTP responses, and CVE-2023-36462, also high-severity, which allows an attacker to configure a verified profile link in a deceptive way that can be used for phishing.
The four vulnerabilities affect all Mastodon versions from version 3.5.0 onward and were fixed in versions 3.5.9, 4.0.5 and 4.1.3.
Patches are security updates for the server and must be applied by administrators to eliminate the risk to their communities.
Information source: bleepingcomputer.com
