

Jimbos Protocol, a DeFi project based on Arbitrum, suffered a flash loan attack that resulted in the loss of more than 4,000 ETH tokens, whose value today exceeds $7.5 million.

The company revealed the attack on Twitter yesterday, saying that law enforcement was notified and that they are working with security professionals to remediate the situation.
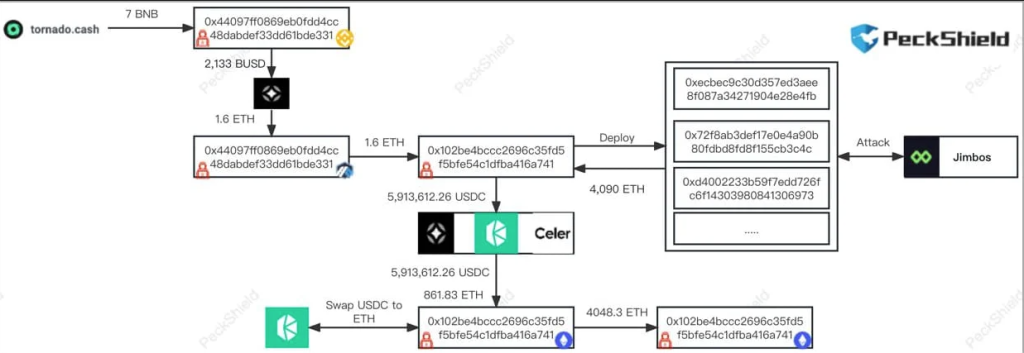
The attack occurred just three days after the platform launched the V2 protocol, at a time when many people had just invested in the “Jimbo” token, and the attacker managed to steal 4,090 ETH tokens.
The jimbo token has a semi-fixed floor price backed by assets, while the platform has implemented mechanisms such as taxes and incentives to help maintain a stable value.
However, after the hack, Jimbo's price quickly collapsed, from $0.238 to just $0.0001.
According to blockchain security experts at PeckShield, Jimbos Protocol fell victim to a flash loan attack that exploited the lack of slippage control on the platform.
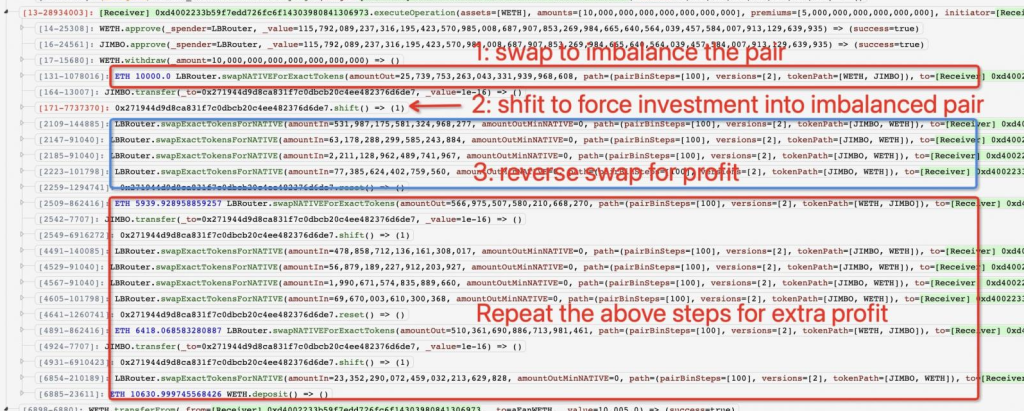
Flash loans are actions in which users borrow a large amount of tokens and are expected to pay them back in the same transaction (immediately).
If the attacker exploits a flaw in the DeFi platform or manipulates the token price during this very short period between receiving the amount and repaying it, they can keep the difference at the expense of the lender.
We have seen this play out many times in theoretically well-secured and meticulously vetted lending protocols – a notable recent example is the flash loan attack that hit Euler Finance, resulting in a massive $197 million loss.
In the case of Jimbos Protocol, the attacker took out a flash loan of $5.9 million, manipulated the market to distort the price range, exchanged the tokens back, and escaped with 4,090 ETH.
Slippage control is a measure that limits changes in token prices to ensure that their fluctuation remains within an acceptable range from the moment a transaction is initiated to its completion - in this case, a flash loan.
Jimbo Protocol had warned investors about the “experimental” nature of Jimbo V1, saying that “the contracts are untested and […] any amount of money you put into this protocol can be lost due to unforeseen circumstances at any time.”
However, Jimbo V2 was reportedly designed to fix slippage and other obvious security issues; therefore, it was presented as a more reliable investment opportunity at least for a short three-day period.
The incident put Jimbo's protocol in a difficult position, and the platform sent an on-chain message to the perpetrators asking them to return 90% of the stolen funds in exchange for a promise not to pursue legal action against them.
Information source: bleepingcomputer.com
