

Security researchers have discovered a new tool used by the FIN7 hacking group to install new versions of the Carbanak backdoor . The malware loader is called BIOLOAD and is quite similar to BOOSTWRITE , another tool that has also been recently linked to the FIN7 hackers. The researchers noted that the loader is not easily detected .
Abuse of legitimate Windows methods
The malware uses a technique called "binary planting," which exploits a Windows for searching for DLLs. This allows attackers to gain more privileges on the system.
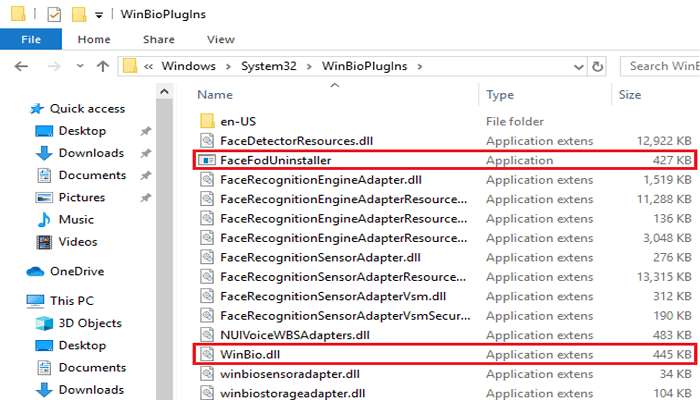
Fortinet 's security platform has blocked malicious payloads in legitimate Windows processes. Specifically, it detected a malicious DLL in FaceFodUninstaller.exe.
“What makes the executable attractive to an attacker is the fact that it was launched from a built-in task, called FODCleanupTask. This reduces the chances of detection,” Fortinet said.
The attacker places the malicious WinBio.dll in the “\System32\WinBioPlugIns” folder, which hosts the legitimate “winbio” DLL.
As mentioned above, the new malware loader BIOLOAD is quite similar to the BOOSTWRITE tool. According to Fortinet, the BIOLOAD samples analyzed appeared in March and July 2019, while BOOSTWRITE was found in May.
However, there are some differences between the two loaders. For example, BIOLOAD does not support multiple payloads. It also uses XOR to decrypt the payload rather than the ChaCha cipher.
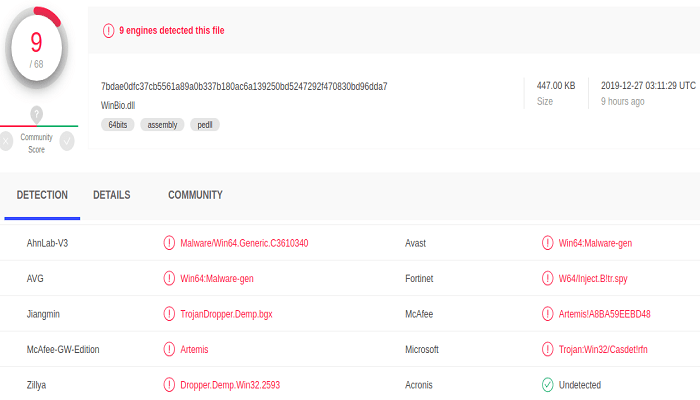
Despite the fact that BIOLOAD has been in use for 9 months, it is not easily detected. Only 9 out of 68 antivirus engines (on the VirusTotal scanning platform) recognize WinBio.dll as malicious.
As for the payload installed on compromised systems, it is a newer version of the Carbanak backdoor.
BIOLOAD, unlike other loaders, checks infected devices for antivirus programs from multiple companies . Other loaders only check for programs from Kaspersky, AVG, and TrendMicro.
Analyzing the codes, techniques, and the backdoor itself, Fortinet attributes BIOLOAD to the FIN7 hacking group.
This is proof that FIN7 is constantly developing new tools to distribute its backdoors.
