

 Security researchers have discovered a hacking group associated with the government Chinese that is carrying out attacks by bypassing two-factor authentication (2FA).
According to a report by Dutch company Fox-IT, the hacking group is known in cyberspace as APT20 and works for the Beijing government.
Key targets of the attacks are government entities and managed service providers (MSPs), operating in sectors such as aviation, healthcare, finance, insurance and energy.
Hacking incidents related to APT20
According to Fox-IT, APT20 began its activities in 2011, but researchers lost track of it during 2016-2017, because the hackers changed their modus operandi.
What has APT20 been doing for the last two years?
According to the researchers, the hackers used web servers as the initial entry point into the systems targets' . In fact, they focused on JBoss , an enterprise application platform often used in large corporate and government networks.
APT20 hackers exploited vulnerabilities that gave them access to servers. They then installed web shells and spread inside victims' systems.
then stole passwords and sought out administrator accounts to maximize their access. They also sought VPN credentials to escalate access to more secure areas of the victim's network.
Despite all this, the hackers managed to remain unnoticed for these two years.
They achieved this by using legitimate tools that were already installed on hacked devices, thus going undetected by antivirus programs.
APT20 bypasses two-factor authentication (2FA)
Researchers found that APT20 hackers compromised VPN accounts that were protected with 2FA.
How they did it is not yet known. However, researchers have made a hypothesis. They believe that APT20 stole an RSA SecurID software token from a hacked system and used it to generate valid one-time passwords and bypass 2FA.
To use one of these software tokens, the user would need to connect a physical device (hardware) to their computer. The device and software token are capable of generating a valid 2FA code. If the device is not present, the RSA SecureID software will generate an error.
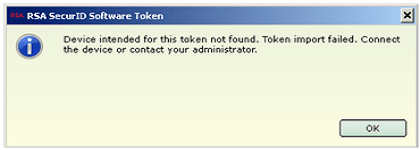
How did hackers overcome this issue? Fox-IT researchers explain:
The software token is created for a specific system, but hackers have access to the victim's system, so things are simple.
All hackers need to do to use the codes for two-factor authentication (2FA) is steal an RSA SecurID Software Token.
Operation Wocao
Fox-IT researchers said they were able to discover the APT20 attacks because one of the victim companies requested an investigation into a hacking incident.
More details about these attacks can be found in a report called “Operation Wocao”.
The hackers try to run various commands on Windows. When the commands fail, the APT20 hackers realize they have been caught and type one last command, wocao, which is Chinese slang for "get!"
