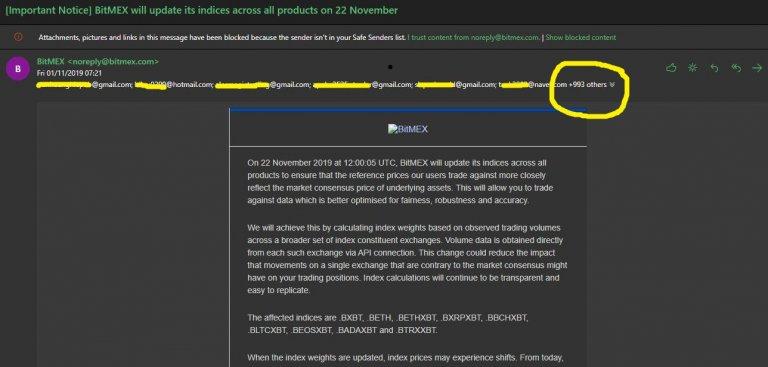
Bitcoin exchange BitMEX accidentally leaked thousands of user emails using the wrong email tool. Instead of using a blind carbon copy (Bcc), it used CC for multiple emails sent to a large portion of user , each containing thousands of user emails, according to reports.
In a statement, BitMEX said: “We are aware that some of users have received a general user update email earlier today, which contained the email addresses of other users.”

“Our team acted immediately to mitigate the issue and we are taking steps to understand the extent of the impact. Rest assured that we are doing everything we can to determine the root cause of the error and will be in touch with all users about the issue ,” he added.
It appears that the email list was split into groups, with some users receiving a portion of other users’ emails and others seeing other emails. As a result, some commentators have claimed that hackers will try to piece together all of the email segments to obtain the full database of leaked emails. The end result could be a phishing attempt,where hackers pretend to be real users using the information they have gathered.
Jake Chervinsky, general counsel at Compound Finance , tweeted , “This is a massive privacy breach with potentially serious consequences for many users and of course the company.”
Just a few months ago, Binance revealed that some of the known-customer documents it had stored on a third-party service had been stolen and made public. It offered 300 bitcoins as a reward for information about the hacker. Binance has also faced two phishing attacks in the past.