

Google revealed Wednesday that it spent $2.9 million in 2017 as part of its bug bounty program that rewards security researchers for finding vulnerabilities. Since the program began in November 2010, Google said it has paid out nearly $12 million to various security researchers.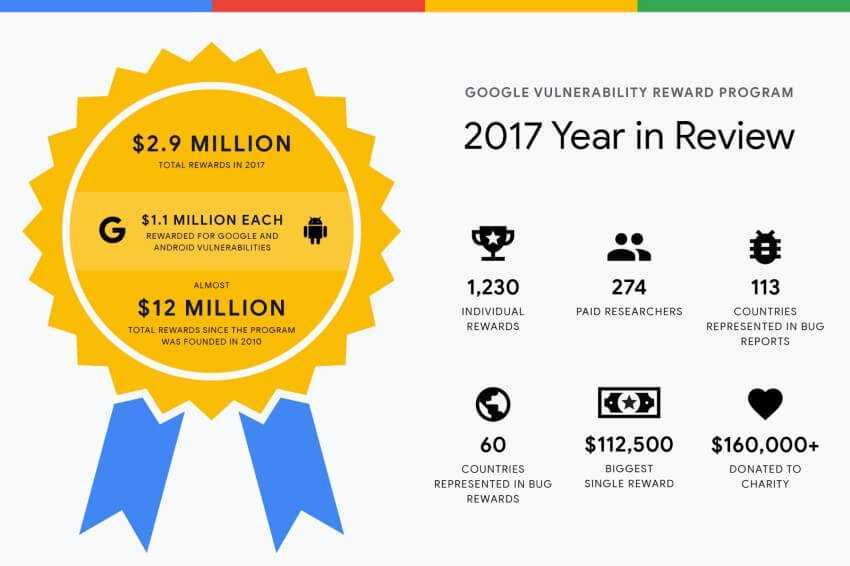
In 2017, Google rewarded a total of 274 researchers in its 2017 bug bounty program, and its largest payout, worth $112,500, went to a security researcher for reporting an exploit chain that could be used to compromise Pixel mobile devices.
Google and Android vulnerabilities each brought in $1.1 million in 2017, while the rest of the money went to Chrome vulnerabilities, the company said in a blog post.
Google also highlighted two other major vulnerabilities discovered in 2017:
Researcher “gzobqq” managed to get $100,000 for a chain of bugs in five components that allowed remote code execution in Chrome OS, and
Alex Birsan discovered that anyone could have gained access to internal Google Issue Tracker data and managed to earn $15,600.
Read the official announcement
- Cloud: Online storage or secure storage?
- Cloud: Google Drive, Dropbox or OneDrive. Which is best?
- Google Drive or OneDrive: What do I choose and why?
