

Recently, a sample of the BlackEnergy Trojan was posted on Google's VirusTotal service, which offers free scanning of files with multiple antivirus engines.
This is a variant of a previous threat, which, according to F-Secure, has distanced itself from the characteristics of a rootkit since it does not hide itself from files and registries. However, the analysis of the sample includes latent routines that hide processes.

This relies on direct kernel object manipulation (DKOM), a method used by various rootkits to hide malicious processes in drivers or files.
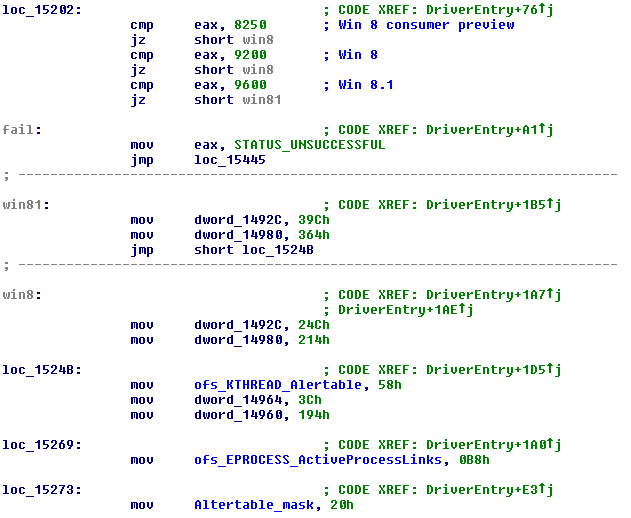
This is why "malware keeps a hard-coded list of compensatory benefits in kernel structures" so it can run on multiple versions of Windows.
According to the F-Secure report, the Trojan has been adapted to support the latest versions of the Windows operating system, 8 and 8.1.
Created by a Russian hacker, the BlackEnergy malware has been used in cyberattacks against Georgia since 2008.
There is no information about whether the threat is currently circulating, but since it has been posted on VirusTotal, there is a good chance that antivirus vendors have already prepared updates for detection and disinfection routines.
Additionally, the sample is not digitally signed, which makes it more difficult to infect a system due to the verification mechanism in modern Windows. However, if this feature of the operating system is disabled, attackers can take over the computer via Black Energy.
