

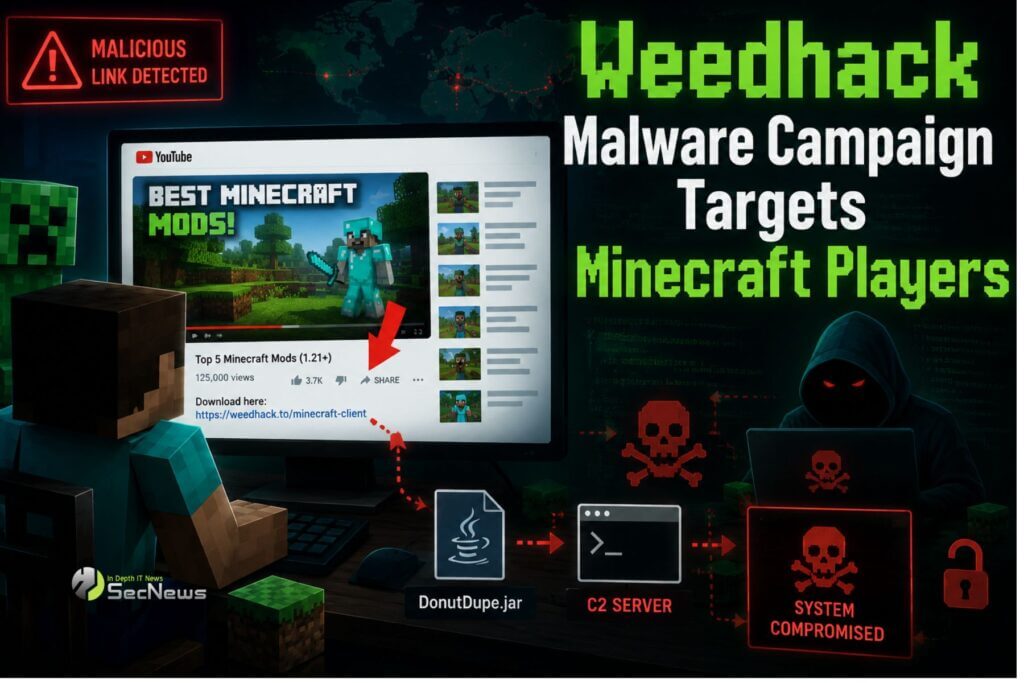
Minecraft players are once again being targeted by cybercriminals, as researchers have identified active campaigns distributing Weedhack through fake clients, mods, and cheats . The tactic is based on copying popular tools and promoting deceptive websites, with the aim of tricking users into believing they are downloading a legitimate program.

McAfee Labs says it blocked more than 6,300 attempts to access malicious websites related to the campaign. What's particularly concerning is the professional way in which many of these pages are designed.
Weedhack malware: Clone websites that look authentic
The fraudulent websites copy the appearance and structure of real projects. They include logos, detailed descriptions of features, FAQs, installation guides, references to the creators, and even links to authentic GitHub repositories.
In this way, attackers try to create an environment that inspires trust. A user searching for a Minecraft client or a popular mod can easily assume that they are on the official page, especially when the malicious domain appears high in the search results.
See also: Weedhack: New malware attack targets Minecraft players
Another feature of the campaign is the use of modern website creation tools. McAfee detected, among others, a page created using Lovable, an AI website development platform. This development shows that artificial intelligence can also be used by malicious actors to quickly create persuasive infrastructures.
SEO poisoning: When Google becomes a trap
Weedhack was first detected in June 2026, with researchers documenting extensive use of SEO poisoning. The perpetrators attempt to artificially improve the rankings of fake websitesso that they appear in the top positions when a player searches for a specific client or mod.
In some cases, deceptive pages for Xenon Client and Nova Client appear high on Google, Bing, Brave Search, and DuckDuckGo. Thus, searching for a simple application can lead directly to malware.
The problem is compounded by the fact that users often assume that the first results of a search engine are safe. However, a high ranking is not proof of authenticity.
From Discord and GitHub to file-sharing services
Weedhack's distribution isn't limited to fake websites. According to McAfee, around 49.6% of the malicious URLs detected were related to Discord, followed by MediaFire at 23.4% and GitHub at 8.2%.
Links are also being circulated via Reddit and other communication channels, while malicious JAR files have been detected on platforms used by the Minecraft community for mods and tools.
See also: SEO Poisoning Attack Deploys Gootloader Malware
Among the domains that have been used are imitations of Glazed Client, Radium Client, Meteor Client, Xenon Client and Nova Client, as well as pages that present themselves as tools for cracking seeds or as mod libraries.
What does Weedhack do on the computer?
The infection is not limited to the installation of a suspicious file. The attack chain ends with JAR payloads that can collect system information, modify security settings, and attempt to gain access to sensitive data.
🔒 Protect your privacy with Proton VPN
Swiss VPN from the creators of Proton Mail — strict no-logs policy, strong encryption, and built-in NetShield that blocks ads, trackers, & malware.
- ✔ No-logs, based in Switzerland (except 14-Eyes)
- ✔ NetShield: blocks ads, trackers & malicious domains
- ✔ Covers all devices — free version available
The link is an affiliate link — SecNews may receive a commission at no additional cost to you. It does not affect the independence of our article writing.
Particularly dangerous is the ability to create exceptions in Microsoft Defender, as such an action can reduce device protection and allow subsequent payloads to execute with less chance of detection.

How Minecraft players can protect themselves
This campaign reminds us that mods, cheats, and clients should be treated like any other software. The safest option is to download them exclusively from the developer's official website or from trusted platforms.
At the same time, you should not disable your antivirus because a program asks for it to be installed. Suspicious JAR files need to be checked before execution, while the device and operating system should remain up to date.
See also: BadIIS malware spreads via SEO Poisoning
The Weedhack case ultimately shows that the popularity of gaming is a significant incentive for cybercriminals. The more players looking for free clients, mods, and cheats, the greater the value of a well-designed fake page. And with the help of SEO poisoning, social platforms, and now AI content creation tools, the trap can be much closer to the actual search result than you might expect.
