

Remote work has become an integral part of modern business life, offering flexibility and reducing the need for a physical presence in the office. At the same time, however, it moves a significant part of corporate security outside the traditional boundaries of the organization. An employee's computer, home Wi-Fi, collaboration applications and even a personal USB can be entry points for cybercriminals.
Safe teleworking doesn't necessarily require expensive solutions. It mainly requires proper organization, clear rules, and consistency. Here are five key steps that can significantly reduce the risks.
Safe teleworking in 5 steps
1. Use a separate and updated device
The first step is to separate, as much as possible, business and personal use. A corporate computer is preferable, as it may have centralized management, antivirus, encryption, and security policies.
See also: How to tell if an email is phishing in 30 seconds
The operating system, browser, and applications should be updated regularly. Cybercriminals often exploit known vulnerabilities for which a patch is already available, but users have not installed it.
At the same time, avoid installing unknown applications and do not disable protection mechanisms just because an application requests it.
2. Secure your home Wi-Fi
Your home network is essentially the gateway to the Internet for most of your devices. Make sure your router uses a strong, unique password and a modern encryption method, such as WPA2 or WPA3.
It is equally important to change the default router administration password and install any available firmware updates .
When working remotely, be especially careful with public Wi-Fi. For sensitive work, use a reliable mobile network or corporate VPN, if provided by your organization.
3. Enable MFA and use strong passwords
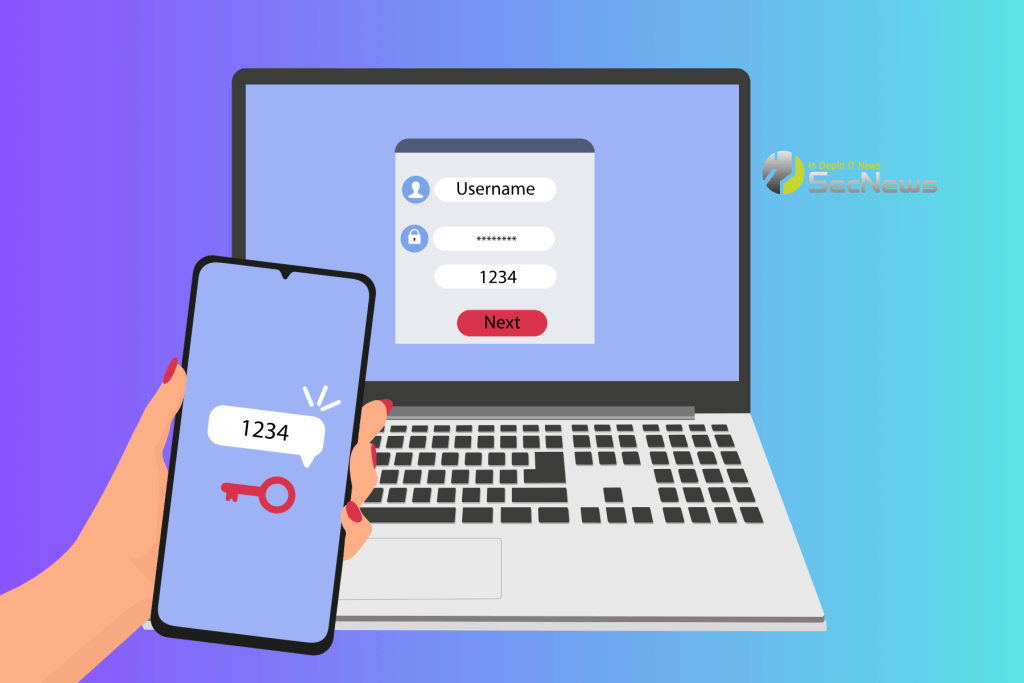
A stolen password shouldn't be enough to gain access to corporate accounts. Enabling multi-factor authentication (MFA) adds an extra layer of protection.
Use different, strong passwords for each service and, where supported, use passkeys. A password manager can generate and store unique passwords without having to remember them all.
See also: What to do if your smartphone is stolen
4. Learn to recognize phishing attacks
Technology can't handle every attack. Many breaches start with an email, message, or link that seems perfectly normal.
Before opening a link, carefully check the sender and the website address. Don't enter codes on pages you've reached via a suspicious email, and don't install software just because a pop-up prompts you to do so.
social engineering attacks powered AI- now require special attention , as messages can be much more persuasive than in the past.
5. Create backups and a response plan
Even with strong protection, no system is completely secure. Important business files should be stored in an approved corporate service and backed up regularly.
It is equally important to know what to do in the event of an incident. If you suspect your computer has been infected, don't try to "hide" the problem. Disconnect the device from the network, if this is required by company policy, and immediately notify the relevant IT or security department.
See also: How to check if your Airbnb or hotel has secure Wi-Fi

Teleworking: Safety starts with everyday behavior
Remote work isn't dangerous in itself. It becomes dangerous when devices, accounts, and data are treated with the same laxity that might exist on a personal device.
With up-to-date equipment, a secure network, MFA, phishing awareness, and reliable backups, you can create a much stronger layer of protection. The most important thing, though, is to treat cybersecurity as a daily process, not something you only need to remember when an incident occurs.
