

JumpCloud, a US-based enterprise software company, is notifying several customers of an “ongoing incident.”.
See also: Microsoft Teams: TeamsPhisher tool exploits bug

The company has revoked existing admin API keys to protect its customer organizations. Affected organizations will need to generate new keys.
Headquartered in Louisville, Colorado, the cloud-based directory-as-a-service platform, launched in 2013, has served over 180,000 organizations in more than 160 countries.
See also: Hacker believed to be a member of the OPERA1ER group arrested
JumpCloud is revoking API keys
This morning, BleepingComputer received a tip from an anonymous reader alerting us to a potential security incident at JumpCloud.
The reader in question is among the JumpCloud customers who received an email from the company today stating that existing admin API keys have been revoked while JumpCloud investigates an “ongoing incident.”
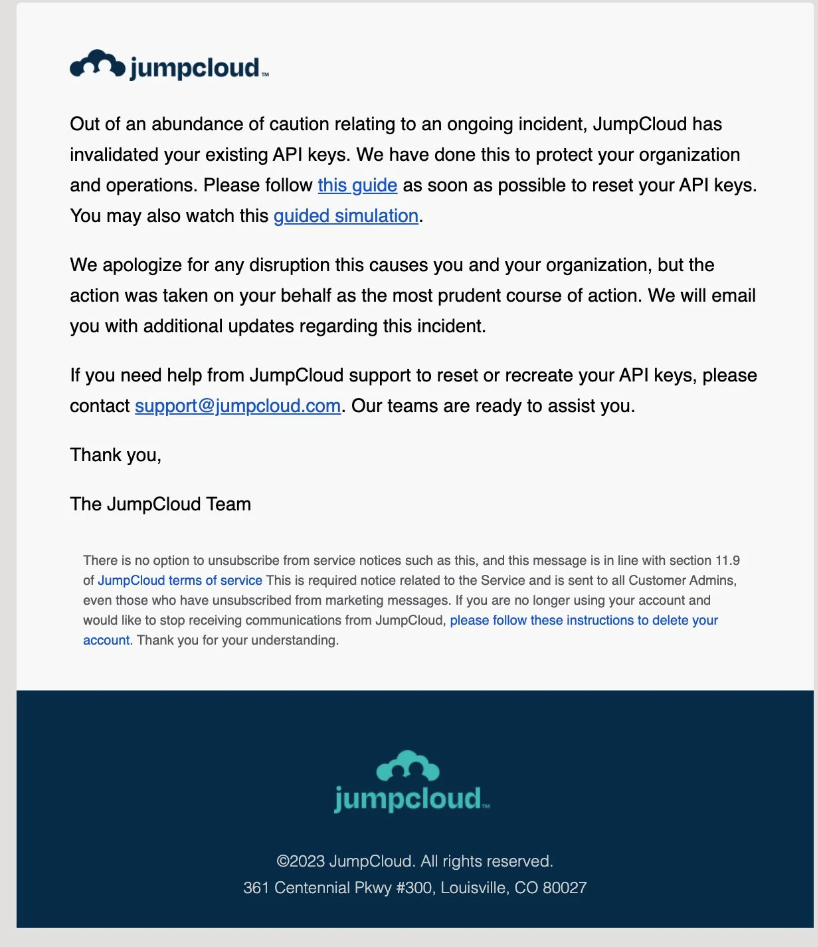
“JumpCloud has revoked your existing API keys. We did this to protect your organization and operations,” the company said in a statement to JumpCloud administrators.
“We apologize for any inconvenience this may cause you and your organization, but this action was taken on your behalf as the most prudent course of action.”
See also: New StackRot Linux kernel flaw allows privilege escalation
The cloud-based security service asked affected customers , specifically administrators who are “currently using their API key or an integration based on a JumpCloud admin API key,” to generate new API keys and update integrations with the new API keys.
Earlier this year, JumpCloud was investigating the potential impact on its customers due to the CircleCI security incident.
Information source: bleepingcomputer.com
