

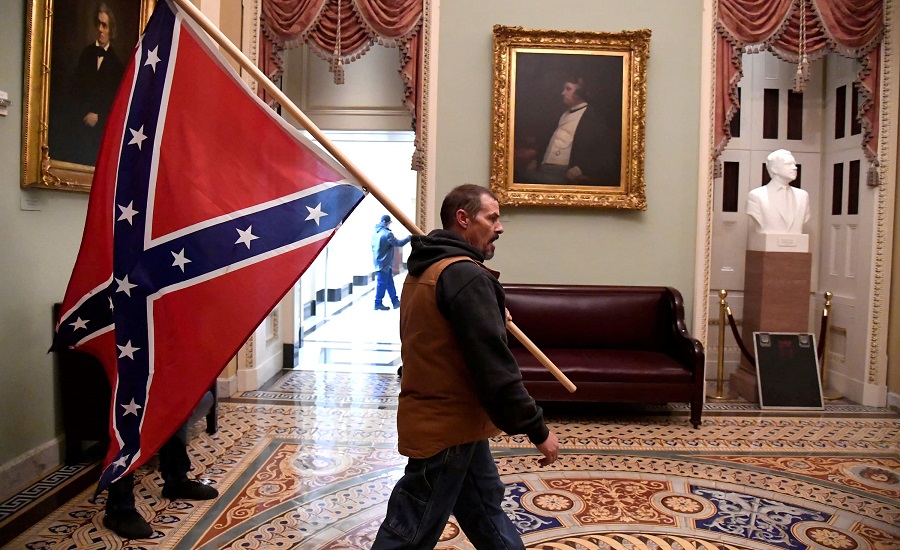
Over the past two days, the biggest news story circulating around the world has been the invasion of the Capitol. Hundreds of Donald Trump attacked the building, while one of them also invaded the private office of the Speaker of the House, Nancy Pelosi. This move was made as a sign of protest against the results of the American elections.

After the notice that politicians and Capitol staff received to evacuate the building, one of the computers they were using was still active and unsecured , while at least one more was stolen from Senator Jeff Merkley 's office .
The attack and computer theft could also be considered a cybersecurity risk. However, most lawmakers do not have direct access to sensitive material unless their job requires it, such as if they are on the judiciary. The computers containing the most sensitive dataare separate and use a different network, and are located in isolated facilities (SCIFs) in inaccessible areas of the Capitol building.
As Mieke Eoyang, a former Intelligence Committee official, stated: “There is no indication that these [classified systems] were breached.”
Despite the assurances, however, the intrusion and theft of electronic material will certainly create confusion in Congress, as it will be necessary to investigate what was stolen and what risks lie ahead for the cybersecurity of the Capitol network. Kimber Dowsett, who has previously worked in the field of government security, said that there was no plan to deal with a possible intrusion into the building.
Of course, the risk to the Capitol's computer network is not as significant as the current espionage campaign against U.S.. And that's largely due to the fact that the majority of Capitol employees are working from home due to the COVID-19.
