


Staples , a large company specializing in the retail sale of office supplies, contacted some of its customers and informed them that there had been unauthorized access to data related to their orders.
For now, not many details have been released, as the company has limited itself to informing affected customers and has not made a public announcement.
Unauthorized access but to “non-sensitive data”
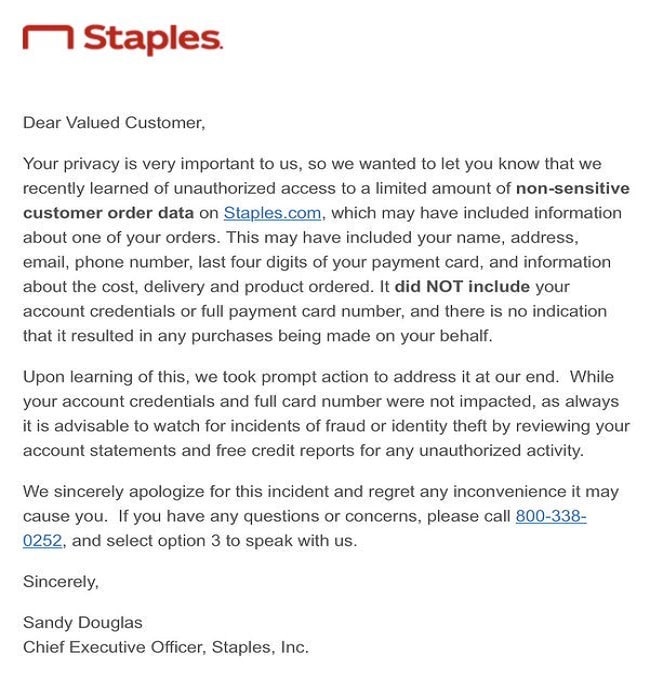
Staples , which primarily sells office supplies and related products, sent a brief letter to its customers outlining the breach . The letter was signed by Staples Inc. CEO Alexander 'Sandy' Douglas .
The breach is said to have taken place around September 2nd.
According to the letter, a limited amount of datarelated to the orders of some Staples customers has been breached.
Staples has yet to identify exactly what was breached, but it says it was “non-sensitive data customer order.” That means it could include: names, addresses, email, phone numbers, the last four digits of a credit card, and order details (delivery, cost, product).

This information may not seem very important, as it can be easily found by anyone. However, it could be useful to cybercriminals for other scams email or phone Hackers could also collect more information to launch a larger attack.
Douglas emphasizes that and account credentials full details customers
According to BleepingComputer, customers who have received the letter can contact Staples directly during business hours.
