

Nearly 2,000 Magento stores have been compromised in the past four days, with security researchers describing the incident as part of the largest campaign ever. In the attacks, hackers compromised sites and then injected malicious scripts into the Magento stores' source code , which records credit card details that shoppers enter into purchase forms.
According to Willem de Groot, founder of Sanguine Security (SanSec), a Dutch cybersecurity that specializes in tracking Magecart, 10 stores were infected on Friday, 1,058 on Saturday, 603 on Sunday and 233 yesterday. De Groot added that this is the largest attack campaign that Sansec has detected since 2015. It is worth noting that the previous record was 962 stores compromised in a single day, last July.
The director of SanSec said that most of the compromised Magento store sites were using version 1.x of the Magento online store software. This is a version that reached its end of life (EOL) on June 30, 2020 and no longer receives updates .
Notably, attacks against sites running the now deprecated Magento 1.x software have been expected since last year, when Adobe – which owns Magento – first issued an advisory in November 2019 advising store owners to update to 2.x. Adobe’s initial warning of impending attacks on Magento 1.x stores was later echoed in similar security advisories issued by Mastercard and Visa in the spring.
At the time, security experts estimated that hackers were waiting for EOL to arrive to make sure Adobe wouldn't fix the bugs – something that ultimately appears to have been verified.
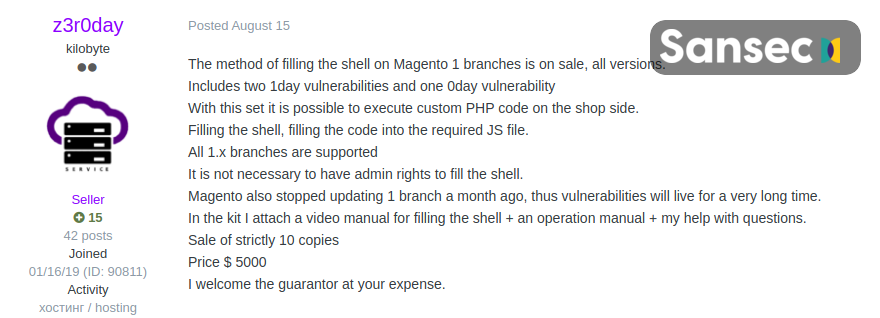
While de Groot has yet to pinpoint how the hackers broke into the sites targeted in recent days, he said that advertisements for a zero-day vulnerability in Magento 1.x had been posted on hacking forums in August, confirming that the hackers were waiting for the EOL to come. In one advertisement, a user named z3r0day offered to sell a remote code execution (RCE) exploit for $5,000, an offer that was considered credible at the time.
The positive thing is that since November 2019 when Adobe started urging Magento owners to migrate to the newer version, the number of Magento 1.x stores has decreased from 240,000 to 110,000 in June 2020 and to 95,000 today.
Furthermore, it is estimated that many of the Magento stores that have not been updated have very low user traffic. Nevertheless, some high‑traffic sites continue to run 1.x and rely on web application firewalls (WAFs) to stop attacks. It is certainly a dangerous strategy that may not prove smart in the long term.
