

Newcastle University, the UK’s leading research university, said the group behind the DoppelPaymer ransomware breached its network, taking systems offline on the morning of August 30. The university added that it will take several weeks to restore its IT services following the hack. The attack is being investigated by the UK police and the National Crime Agency, in collaboration with Newcastle University’s IT Service.
Specifically, the university announced that on Sunday 30 August 2020, it discovered that a serious hack had taken place, which disrupted the operation of its networks and IT systems. As a result, all university systems, with the exception of those referred to in communications (Office365 – including email and Teams, Canvas and Zoom) are either unavailable or available with restrictions. Newcastle University has not yet decided whether to reset account passwords, but says it may do so based on internal support teams and the recommendations of specialist consultants.
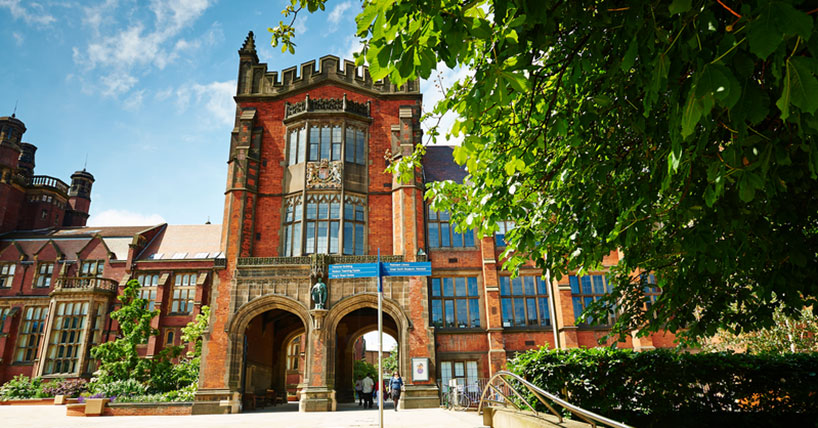
The investigation into the hack is still in an early stage. IT teams continue to work hard to restore systems and cooperate with police and the National Crime Agency in their investigations. However, it is not possible to disclose further details about the incident until this initial investigation is completed. The ICO and the Office for Students were notified within 72 hours of the hack being detected, as a university spokesperson said.
According to the university, at this time many of its IT services are offline and will remain out of operation, while those that are operating could be discontinued without notice during recovery efforts.
Newcastle University also added the following:
- University members may lose access to their IT accounts without notice and may not be reactivated quickly.
- The university may need access to any IT system that its members maintain or use.
- It may be necessary to remove computers, servers , or other devices, if found to be affected, in order to conduct detailed investigations.
During the ongoing investigations, students and staff will only have access to limited IT services, including Office365 (email, applications and Teams comm channels), core SAP services and Zoom. The university has also advised students and staff to copy essential files from the university's shared drive to their OneDrive.
After Newcastle University reported being hacked , the DoppelPaymer ransomware operators claimed responsibility for the incident. They also shared 750Kb worth of stolen data as evidence on the data leak website “Dopple Leaks”, a tactic they have adopted since the Maze Ransomware, since February 2020.
DoppelPaymer is a ransomware operation known to have been attacking companies since at least mid-June 2019, gaining access to admin credentials and using them to compromise the entire network to deploy ransomware payloads to all devices. They are also known to demand large ransoms, as attacks encrypt hundreds or even thousands of systems on their victims' networks.
In November 2019, Mexico’s state-owned oil company PEMEX (Petróleos Mexicanos) was attacked by DoppelPaymer ransomware, with the gang demanding $4.9 million in bitcoins as a ransom for decrypting files. DoppelPaymer is named after BitPaymer, with which it shares large chunks of code, but its operators have added several upgrades to the malware to make it run faster.
