

The French national cybersecurity agency issued a warning yesterday about an increase in attacks targeting private and public administrations across the country. In France, public administration has three sub-sectors: central public administrations (APUC), local government (LUFA) and social security administrations (ASSO).
Emotet, which was originally a bank-of-the-mill Trojan, first appeared in 2014, having now evolved into a malware botnet used by a hacking group known as TA542 and Mummy Spider.
This malware is used by hackers to drop other malware families, including Trickbot – which is used to deploy Ryuk and Conti ransomware payloads – and QakBot trojans on infected systems.
France’s National Agency for Information Systems Security (ANSSI) said it has observed the targeting of French companies and administrations by the Emotet malware for several consecutive days. ANSSI also stressed the seriousness of the situation, given that Emotet is now being used to develop other malware that can have a significant impact on victims. ANSSI also noted that the botnet targets all business sectors worldwide, with attacks on organizations in France suddenly increasing in recent days.
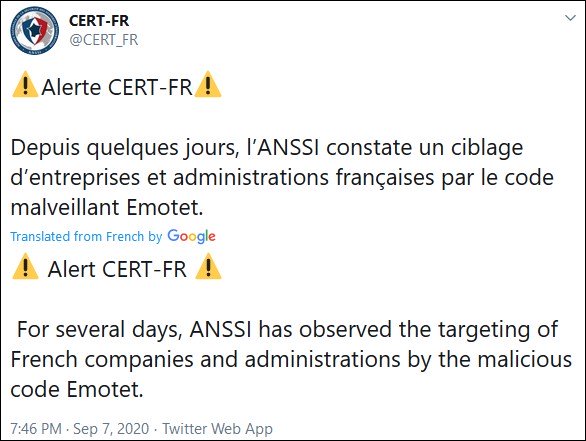
ANNSI also shared a list of steps that it recommends organizations follow to prevent Emotet infections, but also to have a proper response after a potential breach of their systems:
• Inform users not to enable macros in attachments, to be careful about the emails they receive and to reduce the execution of macros.
• Restrict Internet access for all agents to a controlled “white list”.
• Disconnect compromised machines from the network without deleting data.
• Send the samples (.doc and .eml) that you have at your disposal to ANSSI for analysis, in order to identify IoCs that can be reported. This is very important, as the attacker’s infrastructure evolves frequently, so access to recent samples is essential.
This alert comes after the Emotet malware botnet returned with a massive campaign of malicious spam – which can appear as payment reports, invoices, job opportunities, and shipping information – to deliver malicious Word and spreadsheet attachments, starting July 17.
According to researcher James Quinn, Emotet last appeared on February 7, 2020, with the malware remaining “quiet” for five months and not sending spam messages until July. Additionally, Microsoft said that since its reappearance on July 17, Emotet has continued its activities with daily spam messages to more than 500,000 emails every day (excluding weekends) as of 2:00 a.m. Pacific Time (UTC -7).
Since its return, Emotet has started installing the TrickBot trojan on infected Windows, replacing TrickBot payloads and spreading the QakBot malware. According to reports, QakBot will deliver the ProLock ransomware as a payload to some of the systems initially compromised by Emotet. In addition, Emotet, which is a significant threat to companies according to the warning issued by France, uses stolen attachments to improve the authenticity of its malicious emails. It inserts malicious URLs or attachments into new email messages that are attached to existing conversations. Finally, since its re-emergence, Emotet has ranked first in a list of the top 10 malware strains analyzed on the interactive malware analysis platform Any.Run.
