


Over the weekend, hackers launched a massive attack targeting WordPress sites. The attackers are exploiting old vulnerabilities in outdated plugins to steal configuration files from WordPress sites.
Exploiting these vulnerabilities allows downloading or extracting wp-config.php files from unpatched websites and extracting database credentials . Hackers can then use the usernames and passwords to take control of the databases.
Ram Gall, a threat analyst at Wordfence, said that last weekend's attack was huge compared to the attacks and campaigns the company observes on a daily basis.
Gall said that “this campaign represents 75% of the total plugin and theme exploitation efforts in the WordPress ecosystem.”.
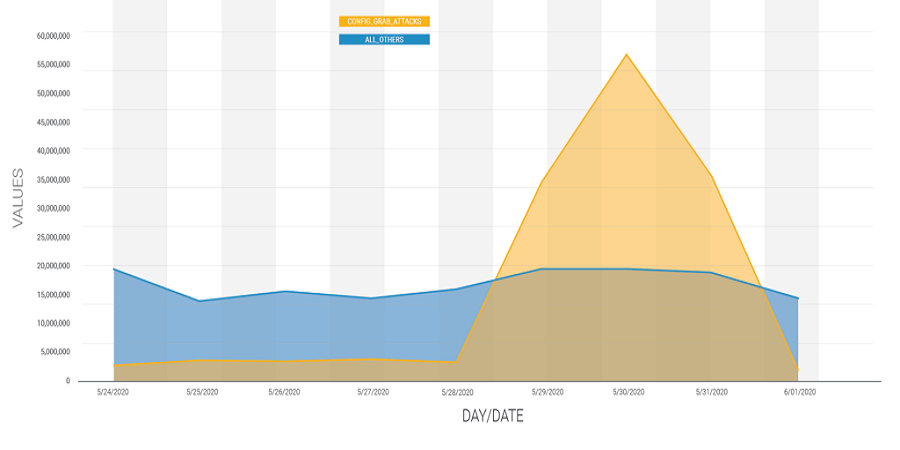
According to Gall, WordFence has blocked more than 130 million attack attempts on its network alone. These attempts targeted more than 1.3 million WordPress websites. However, analysts believe that attackers are targeting even more sites.
The Wordfence analyst said the attacks were carried out from a network of 20,000 different IP addresses. Most of these IP addresses were also used in another similar large-scale campaign targeting WordPress sites in early May.
During the first hacking campaign, the attackers had exploited XSS (cross-site scripting) vulnerabilities and had attempted to introduce new administrators and backdoors to the targeted sites.
The first campaign was also very large, as the XSS attacks exceeded the XSS attacks carried out by other hacking groups in the past (as shown in the chart below).
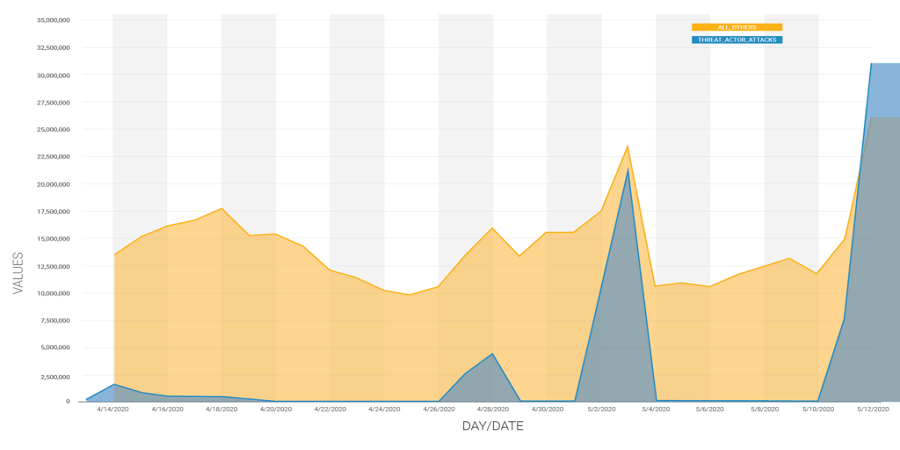
Analyst Gall believes that the two campaigns likely came from the same hackers, despite the fact that different vulnerabilities were used for the attacks.
