

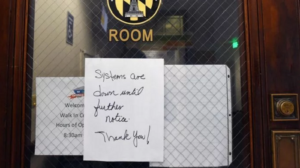
About five days after Baltimore's government was paralyzed by cryptocurrency ransomware that infected computers connected to the city's communications network servers, the hackers were still accessing the network over the weekend, prompting a more in-depth investigation by the FBI, according to Mayor Jack Young.
“These people are so experienced because their job is just to disrupt,” Young said. “I really wish they would use their experience for something better than setting up money scams on cities and companies.”
Last Wednesday, it was reported that hackers had taken down Baltimore's entire communications network.
The Baltimore Sun reported that the ransomware was identified as RobinHood. The hackers demanded encryption as the preferred payment method to unlock files on various computers.
The hackers stated in the note that 3 Bitcoins (about $21,700 at current prices) would unlock each system and about 13 Bitcoins (worth $86,400) would unlock the city's entire communications system.
The note also stated that if anyone from the government contacted the authorities, all communication would be cut off. It also stressed that antivirus software would damage computers. The ransomware processes were entirely automated.
“We won’t say anything more, all we know is MONEY!” the note said. “Hurry up! Tick Tock, Tick Tock, Tick Tock!”
The FBI has not yet released details about the case, but ransomware is suspected to be behind the incident. Here is a statement from the mayor made on Saturday:
“City services have not been affected. People use cash for their transactions or if they can’t do their transactions in person, they send their money through the mail. That’s how the whole city operates. We do it differently and the citizens of Baltimore are not affected terribly, we just can’t get emails and things like that,” Young said. “We do everything manually, like we did a few decades ago.”.
Last week, city administration employees were sent home as their computers were almost unusable.
Max Reuling, a consultant with the Baltimore City Department of Public Works and project manager at TFE Resources, said work was halted last Tuesday after a ransomware attack destroyed emails and critical work programs connected to Baltimore's servers. TFE Resources is a private company responsible for maintaining Baltimore's water and sewer lines. As of Saturday, he said certain communication systems were still down.
As for the ransom, Young said that of course the hackers will not collect a single Bitcoin.
Nearly 22 local government ransomware attacks have been reported in 2019, which so far surpasses the number from 2018.
In March, the New York state capital, Albany, fell victim to a ransomware attack.
Washington has said Iran was responsible for the two most devastating ransomware attacks in the United States, which took place last year in Atlanta and Newark. The ransomware, called SamSam, made off with $6 million from local governments, the Justice Department said, and caused $30 million in damage.
WannaCry and NotPetya were the most devastating infections worldwide several years ago and were allegedly manufactured in North Korea and Russia.
As for local governments in the US, such as Baltimore, they are considered "easy targets" by America's adversaries because their networks are generally not updated as frequently as those of large corporations.
