

Advanced version of Nuclear Exploit Kit exploits a recently patched Flash Player vulnerability
Security researchers have identified an advanced version of the Nuclear Exploit Kit, which has been supplemented with new code that exploits a Flash Playerthat was recently patched by Adobe.
The vulnerability, which has been assigned the identifier CVE-2015-0336, could be exploited for remote code execution on an affected system. The Flash Player was patched on March 12 with the release of versions 17.0.0.134 and 13.0.0.277 (extended support) for Windows and Mac, as well as version 11.2.202.451 for Linux.
A few days ago, Trend Micro security researchers noticed the first traces of malicious activity based on the exploitation of this particular security vulnerability.
According to telemetry data provided by the company, many users have not yet upgraded to the latest version, and are using an earlier, vulnerable version of Flash Player.
“This exploit, which is detected as SWF_EXPLOIT.OJF, is distributed to users via compromised websites, including a website that provides a tool to repair Internet Explorer, as well as various Japanese pornographic websites,” researcher Peter Pi said in a blog post.
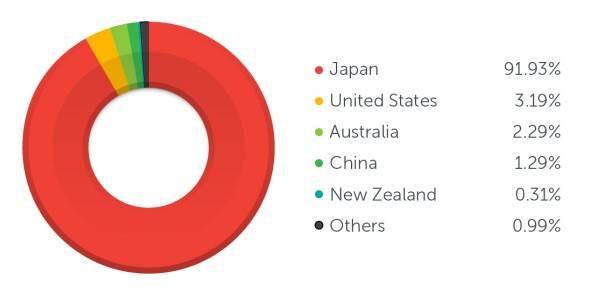
So far, the company has recorded more than 8,700 unique visits to the malicious websites, with the majority of IP addresses (91.93%) originating from Japan. Users from other countries, including the United States, Australia, China, and New Zealand, have also been targeted.
