

The first known Dero coin cryptojacking operation was found targeting vulnerable Kubernetes container infrastructure with exposed APIs.
Dero is a currency promoted as an alternative to Monero with even stronger anonymity protection. Compared to Monero or other cryptocurrencies, Dero promises faster and higher mining rewards, for’ this it has likely attracted the attention of hackers.
In a new CrowdStrike report, researchers explain how the campaign was discovered in February 2023, after noticing unusual behavior while monitoring customers' Kubernetes clusters.
See also: Kinsing malware compromises Kubernetes clusters
Kubernetes scanning
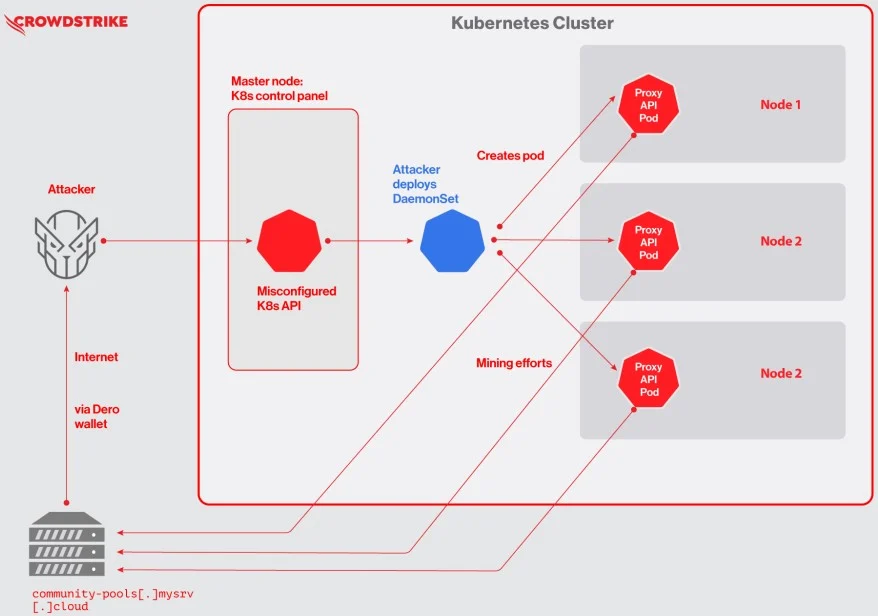
The researchers say the attacks begin with hackers scanning exposed, vulnerable Kubernetes clusters with authentication set to –anonymous-auth=true, allowing anyone to anonymously access the Kubernetes API. Once they gain access to the API, the hackers will deploy a DaemonSet named “proxy-api” that allows the attackers to bind the resources of all nodes in the cluster simultaneously and mine Dero using the available resources.
The installed miners will join a Dero mining pool, where everyone contributes and receives shares from any rewards.
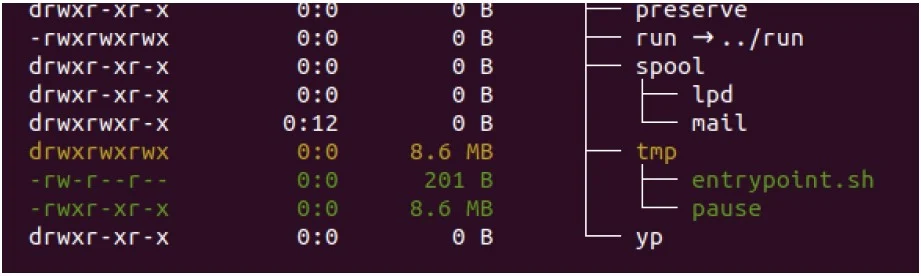
The Crowdstrike says that the Docker image used in the observed Dero cryptojacking campaign was hosted on Docker Hub and is a slightly modified CentOS 7 image that contains additional files named “entrypoint.sh” and “pause”. The first file prepares the Dero miner with a hardcoded wallet address and a Dero mining pool, while the binary “pause” is the actual coin miner.
Crowdstrike analysts have not observed any intent from the hackers to act maliciously and steal data or cause further damage, therefore the campaign appears to have 100% financial motives.
Suggestion: CrowdStrike releases new Azure security tool after failed hack
A regional war
Shortly after Crowdstrike discovered the Dero campaign, its analysts identified a Monero cryptojacking operator who attempted to steal the same resources, ultimately displacing the Dero miner.
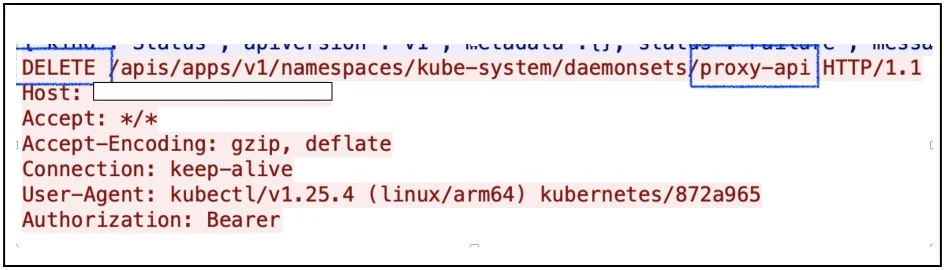
The second hacker deleted the DaemonSet “proxy-api” used by the Dero campaign and then carried out a much more aggressive takeover, using a privileged pod and mounting a “host” directory, trying to escape from the container. Then, he used a custom XMRig miner that he downloaded from the attacker’s command and control server to mine Monero, scaling the host and installing a custom service.
The Monero campaign chose to mine on the host instead of the pods, as Dero did, to gain access to more computing resources and to reap a more significant profit. Also, running mining processes on the host makes them harder to detect if they are properly disguised as system services.
Read also: Crowdstrike compensates up to $1,000,000 in case of data breach
Finally, the operator set up a cronjob to trigger the payload, thus ensuring persistence between Kubernetes cluster restarts. While cryptojacking campaigns are nearly a dozen, mining Dero against other privacy coins, such as Monero, makes it a new campaign.
source of information:bleepingcomputer.com
