

Delaware County, Pennsylvania, has paid a $500,000 ransom to hackers who infected systems with DoppelPaymer ransomware over the weekend. Earlier this week, the county revealed that it had taken parts of its computer network offline after a breach. Additionally, the county said that its Board of Elections and emergency services department were not affected by the attack and are on a different network than the compromised systems.
Local media reported that the operators of the DoppelPaymer ransomware gained access to networks containing police reports, financial and commercial data, and other databases. The hackers behind the attack demanded a ransom of $500,000 to provide the Pennsylvania county with a decryptor.
DoppelPaymer ransomware is known to steal unencrypted files during its attacks, but it is not yet known whether this was the case in the attack that took place in Delaware County, Pennsylvania.
As BleepingComputer reports, it was also learned that the ransomware gang advised the Pennsylvania county to change all passwords and modify its Windows domain configuration to include safeguards from the “Mimikatz” program. Mimikatz is an open -source commonly used by ransomware gangs to harvest Windows domain credentials on a compromised network.
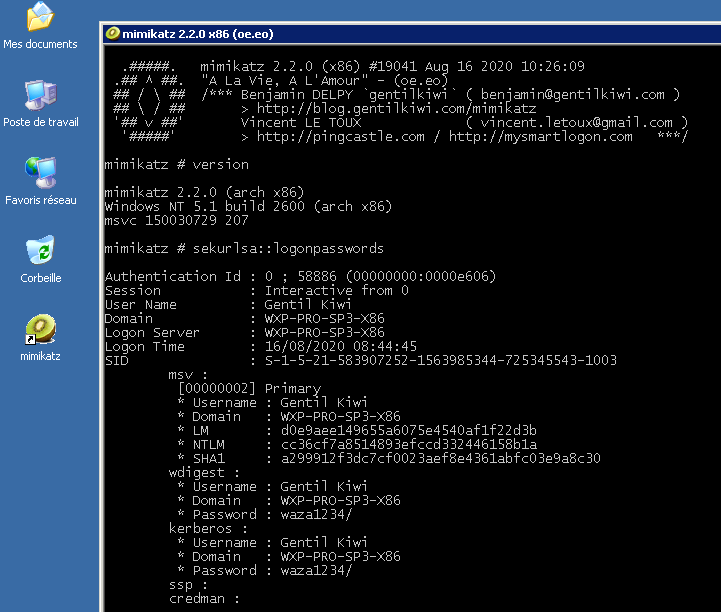
Once hackers gain access to a Windows domain administrator password, they deploy their ransomware to the network to encrypt the devices on it.
SANS ISC has shared an article on how to secure a Windows network against Mimikatz attacks, which all Windows network administrators should be familiar with.

Delaware County, Pennsylvania, joins the list of victims attacked by the DoppelPaymer ransomware. Among them are Compal, PEMEX (Petróleos Mexicanos), the city of Torrance, California, Newcastle University, Hall County, Georgia, Banijay Group SAS, and Bretagne Télécom.
