

A short while after the disclosure of the security vulnerabilities found in the Intel Management Engine, several manufacturing companies are responding by completely disabling this technology from their new products.

The Intel Management Engine is a technology that many describe as an operating system embedded within a processor. The tasks of the IME are autonomous from the main operating system, having its own file system, memory management, and many other things. Therefore, a hacker can easily gain full access to the user's computer. Below are the processors it concerns:
• 6th, 7th and 8th generation Intel Core Processor Family
• Intel Xeon Processor E3-1200 v5 and V6 Product Family
• Intel Xeon Processor Scalable Family
• Intel Xeon Processor W Family
• Intel Atom C3000 Processor Family
• Apollo Lake Intel Atom Processor E3900 Series
• Apollo Lake Intel Pentium Processors
• Intel Celeron G, N, and J series Processors
The first company to make the decision to disable the technology is Purism, which is now using a new technique discovered by researchers at Positive Technologies to protect its customers.
The second company is System76, which sells computers with a custom Linux. The versions that will need to be updated are Ubuntu 16.04 LTS, Ubuntu 17.04, Ubuntu 17.10 and Pop!_OS 17.10.
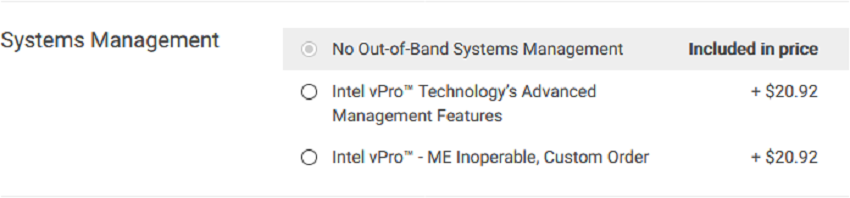
A similar policy was followed by Dell , which gives the consumer the option to purchase a computer without even the Intel Management Engine.
On the other hand, Acer, Fujitsu, HP, Panasonic and Lenovo promised to fix this security vulnerability with a future patch.
