

Security researcher Michael Gillespie has created a decrypter that can recover files locked by the MIRCOP ransomware, without having to pay any money.
The MIRCOP ransomware appeared towards the end of June and had two unique features that made it stand out from all the ransomware variants discovered every day.
One of them is the ransom note, which uses the masked Guy Fawkes figure, commonly used by Anonymous hackers.
The ransom note has a threatening tone and informs the user to return the stolen money or face consequences, allegedly from the Anonymous hacker who has been robbed.
The second feature was the exorbitant amount of money requested in the ransom note, which was 48.48 Bitcoin ($32,000).
Three days after Trend Micro and Nyxbone security researcher revealed the presence of this new family, Gillespie had already created a decrypter for this threat.
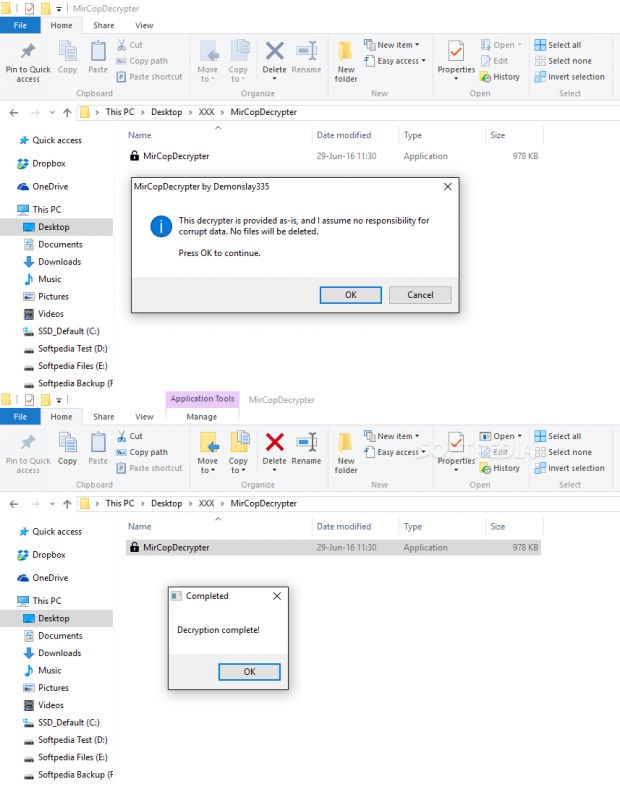
You can download the decrypter by clicking here. Simply unzip the zip file and run the application.
Decrypter will leave the original encrypted files in place, just in case the decryption routine fails, so you can use it without fear of losing your original files.
Once the decryption is finished, you will receive a notification message on your screen, like the one pictured below.
In case you need help with Decrypter, Gillespie provides you with the necessary support in this Forum.
